Microsoft 365 reports for every client, without the busywork
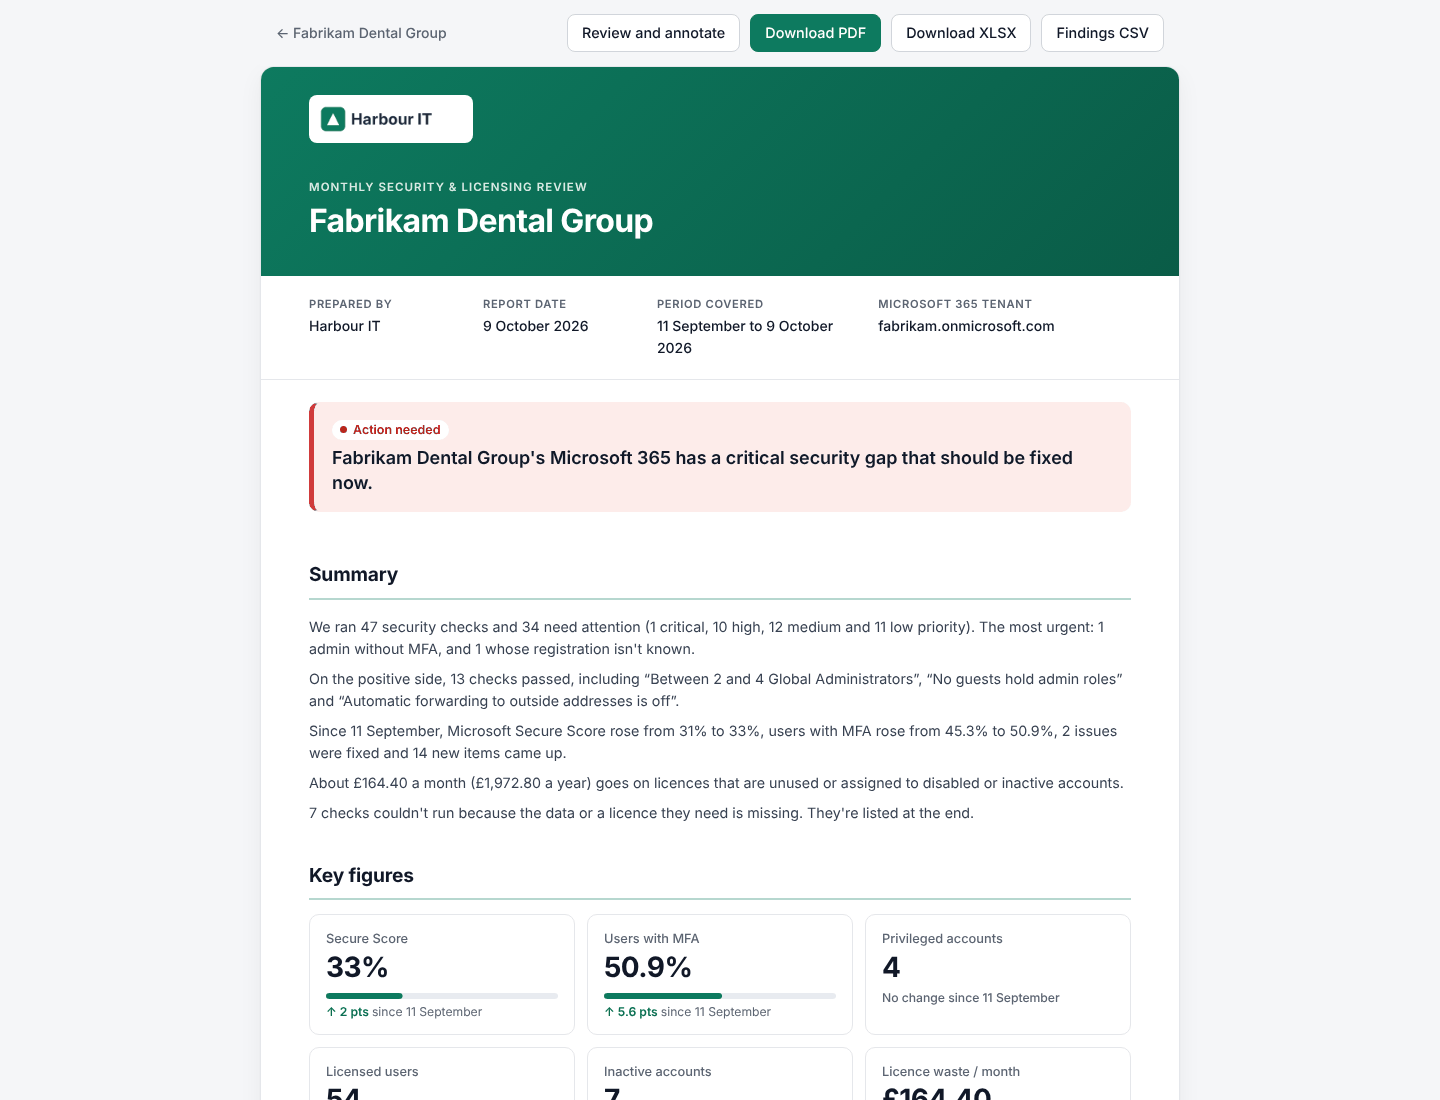
Office Sentry reads each client's Microsoft 365 tenant every night, keeps the history and turns it into the reports you actually send: a branded monthly review, client reports you design yourself, evidence for Cyber Essentials and insurance forms, 53 detail reports, a page for every person, mailbox, group and site, a view across every client and what changed since last month.
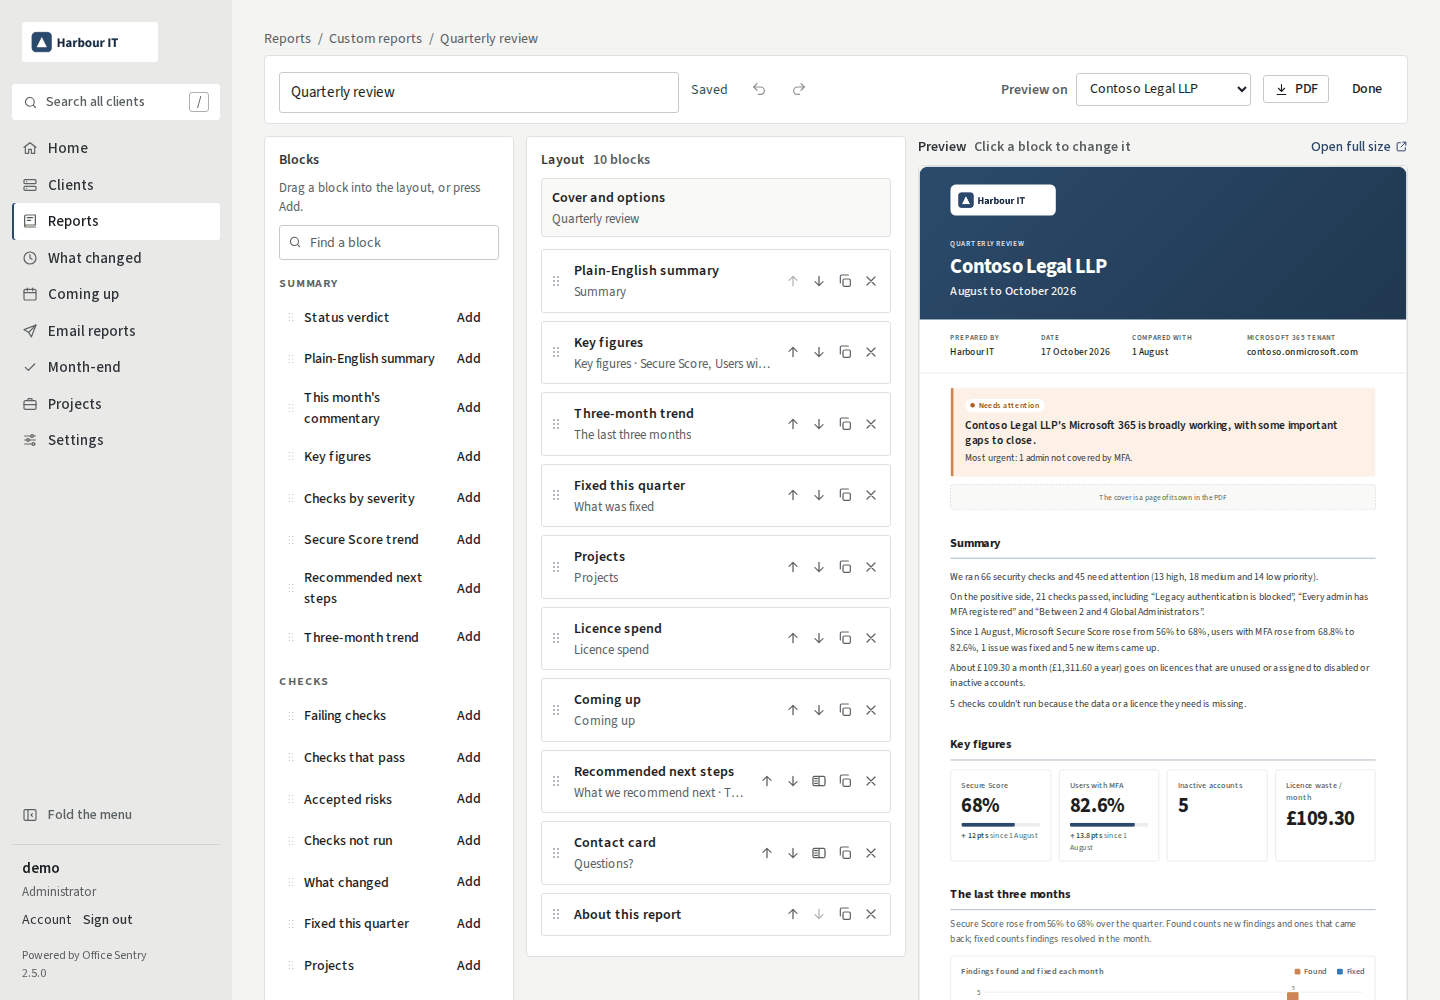
Pick the blocks you want, put them in order and watch the report fill in with a real client's data as you go. One custom report works for every client, carries your branding, and a report plan or a client's email schedule can send it as a PDF.
Blocks for everything a report needs: a verdict, key figures, failing checks, what changed, licence spend, a table from any detail report and your own text
Drag blocks in, set each one up and put two side by side
Preview it on any client at the printed page's size, with undo and redo, and download the PDF in one click
Start from an executive summary, a full review, a licensing review or the Quarterly review (example PDF)
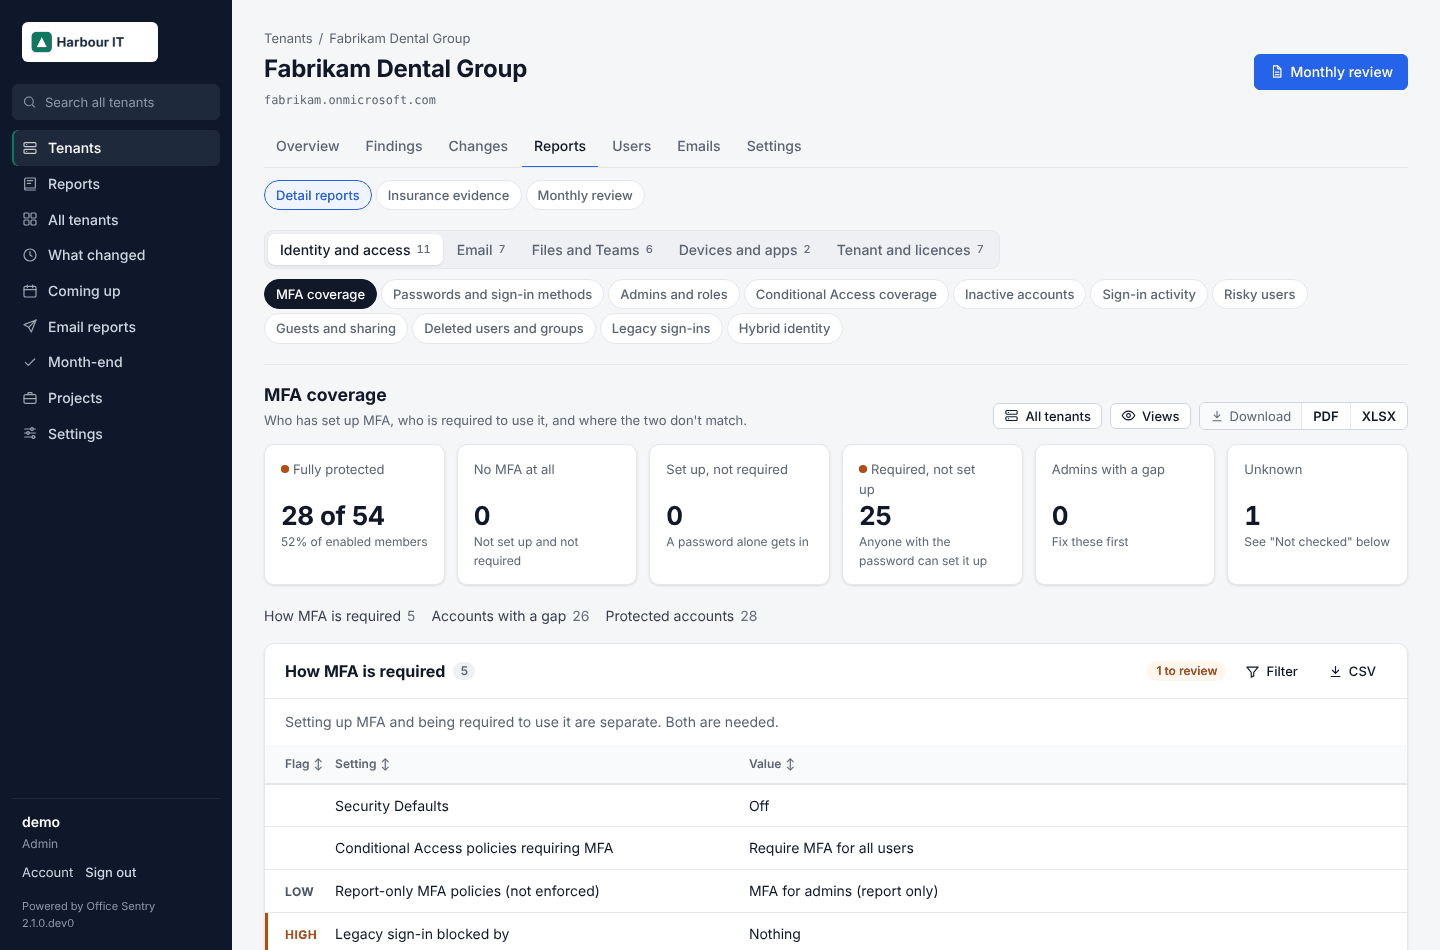
Identity, email, files and Teams, devices and licences: MFA coverage, mail forwarding, mailbox permissions, mail flow per domain, mail flow rules and spam protection, sign-ins, Conditional Access and the organisations and networks it trusts, administrative units, Teams channels and their guests, who can reach each SharePoint site, Intune policies, BitLocker recovery keys and remote access tools on managed devices, Defender alerts, Microsoft 365 outages, licence changes month by month, licence right-sizing and more.
Filter by any value or date, sort and hide columns
Tables fit a laptop: wide reports open on their key columns, and long lists fold to a short form
Save a view and reuse it on any client
PDF, XLSX and CSV downloads contain exactly the rows shown
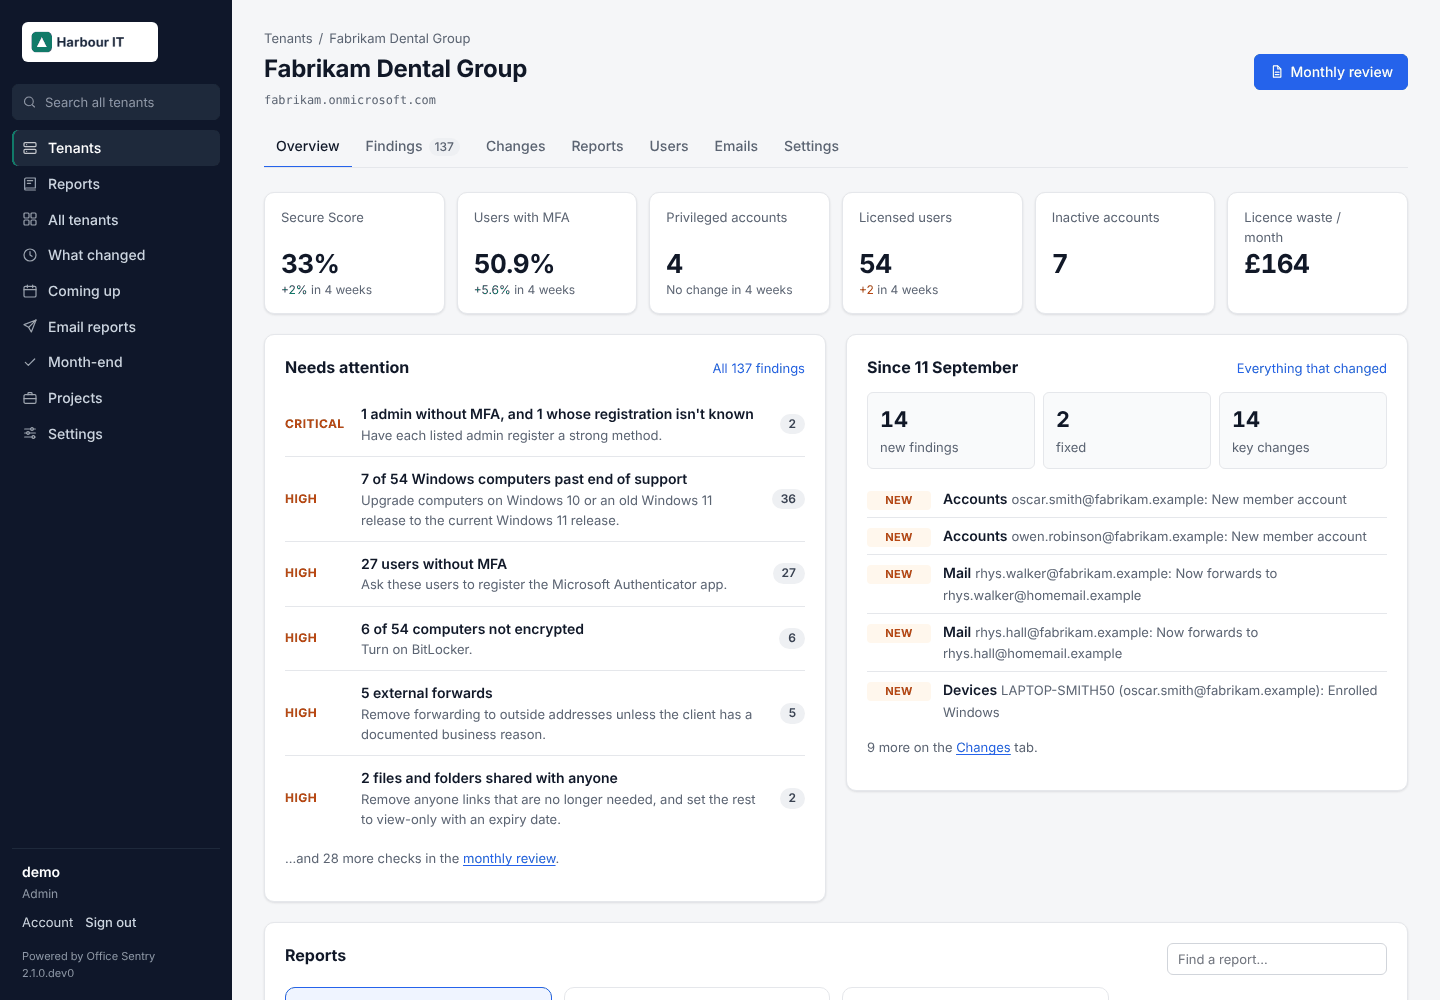
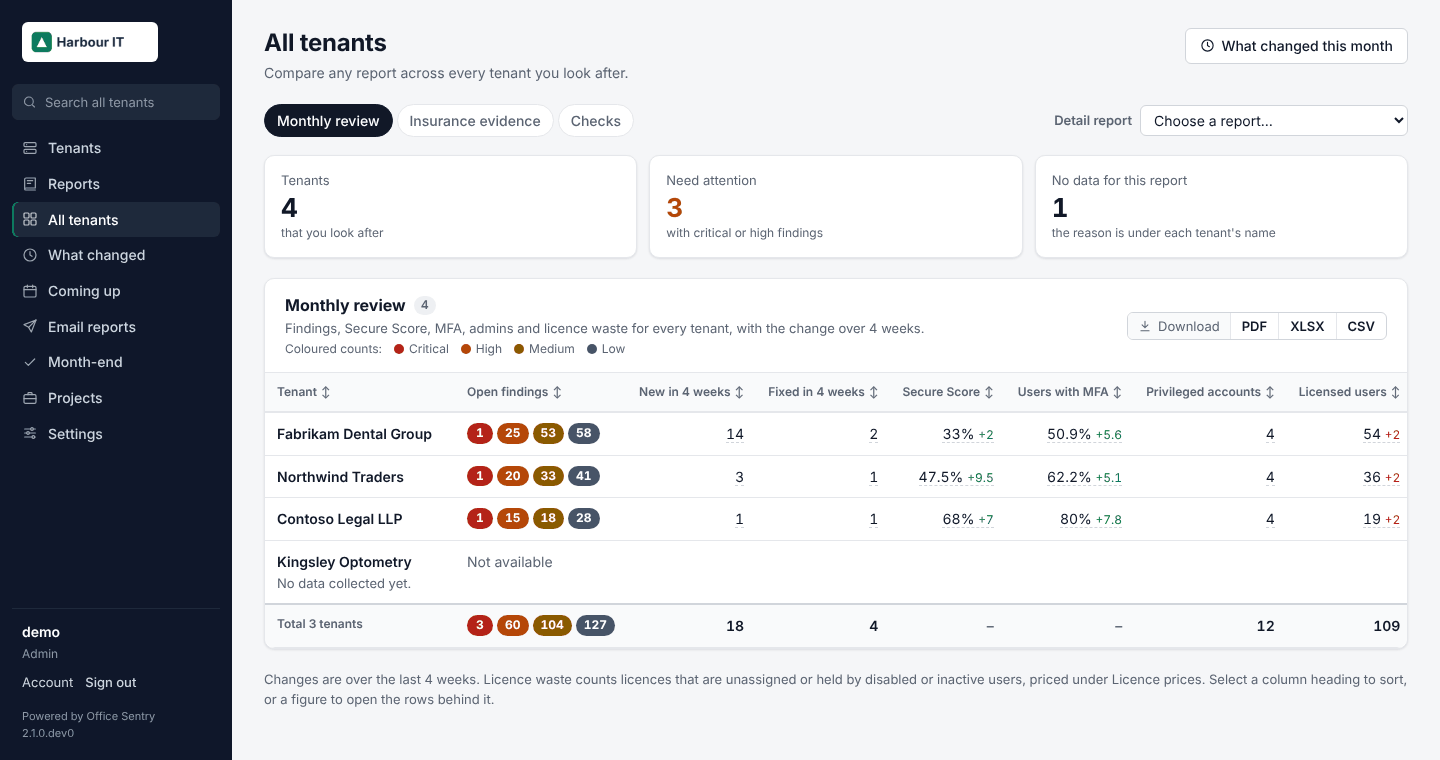
Clients puts every client side by side, worst first, and its menu compares any report across every client, one row each. What changed lists the month's changes, most important first: new and fixed findings, admins, accounts, Conditional Access, forwarding, apps and devices.
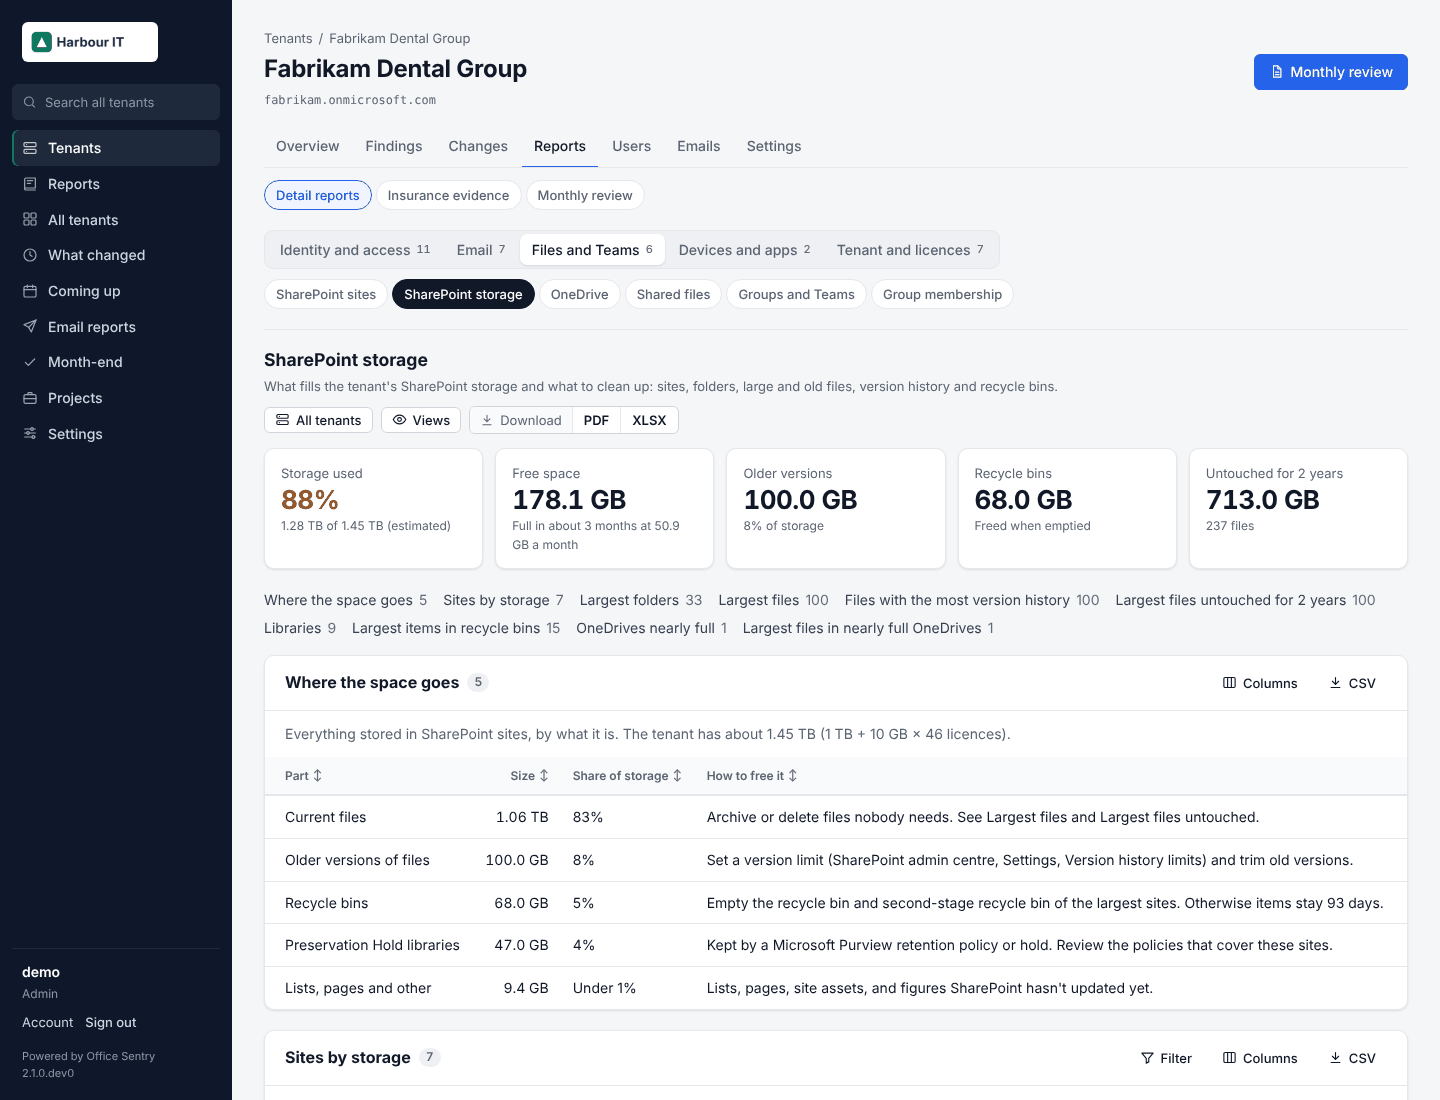
SharePoint storage: why it's full and what to clean up
See how full a client's SharePoint is and when it will run out at the current rate, where the space goes, and the biggest folders, files, version histories and recycle bin items, each with what to do about it.
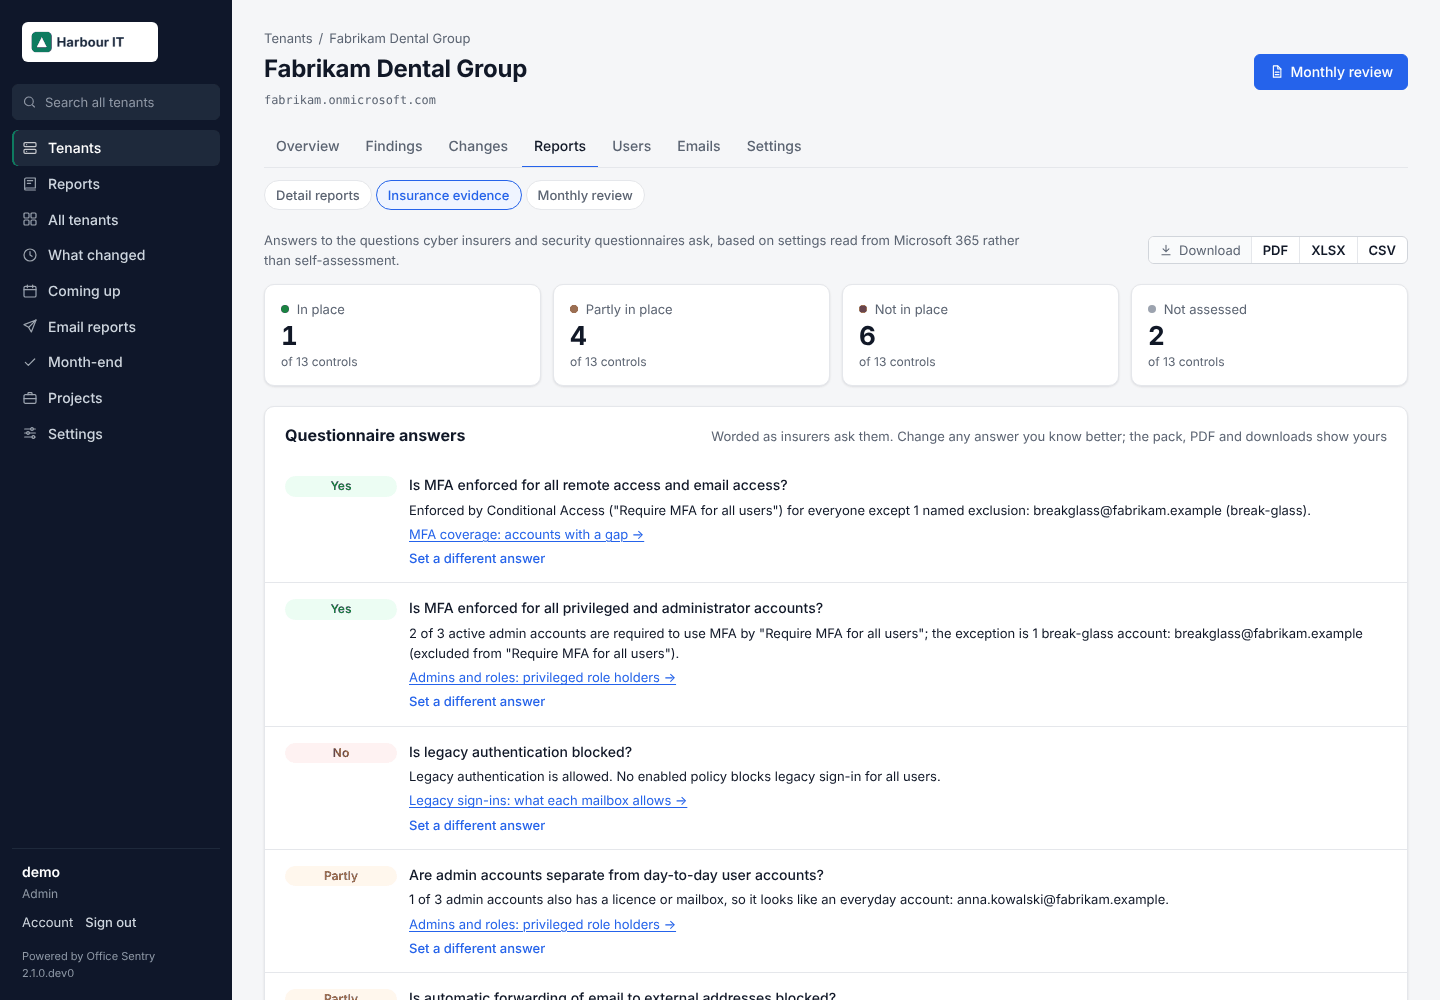
Cyber Essentials, ISO 27001 and insurance evidence, answered from the data
Cyber Essentials and CE Plus are judged from the data control by control, with what to fix before applying and the answers for the IASME portal ready to paste. The insurance evidence pack answers the controls cyber-insurance questionnaires ask about, such as MFA, admin accounts, legacy sign-in, email authentication, forwarding, leavers and devices, with the gaps listed, and so does the supplier security questionnaire. IASME Cyber Assurance, ISO 27001 Annex A, UK GDPR, the CIS Microsoft 365 benchmark, NIST CSF 2.0, SOC 2 and the Essential Eight are judged the same way, with the governance answers left for you to complete.
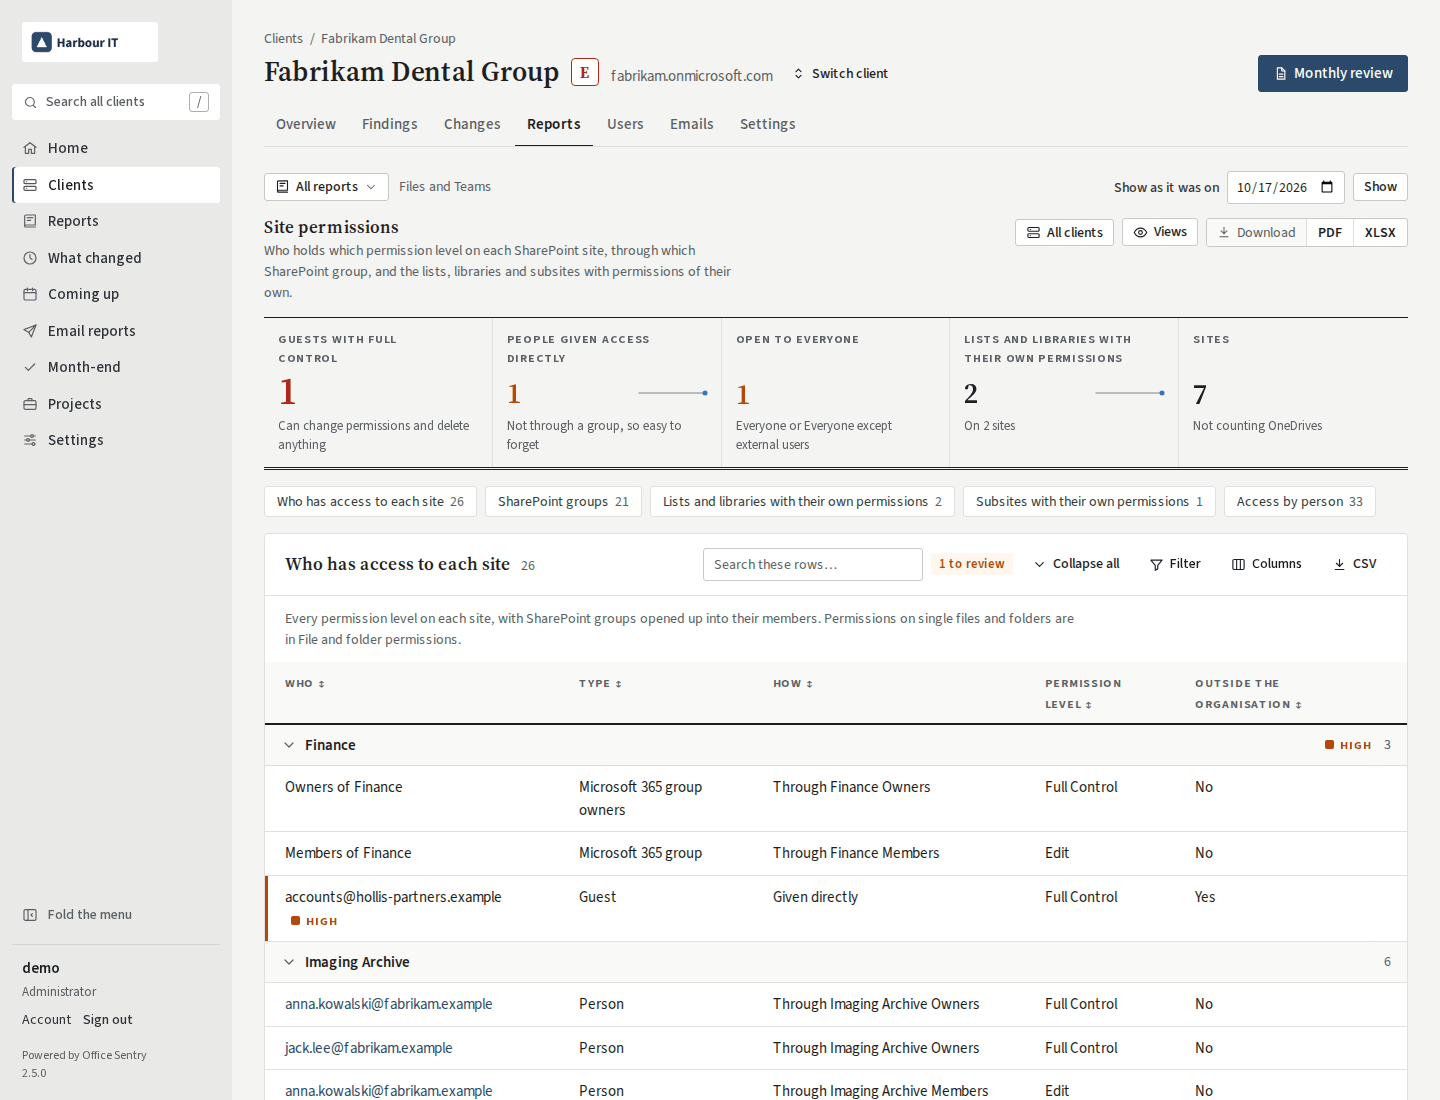
Three reports answer it, from the site down to the file, with guests and people outside first.
Site access: owners, administrators, members and guests of every site
Site permissions: SharePoint groups, permission levels, and lists and subsites with their own
File and folder permissions: who shared what and when, and links past their expiry
A check for guests with full control, and for people outside who can edit
A page for every person
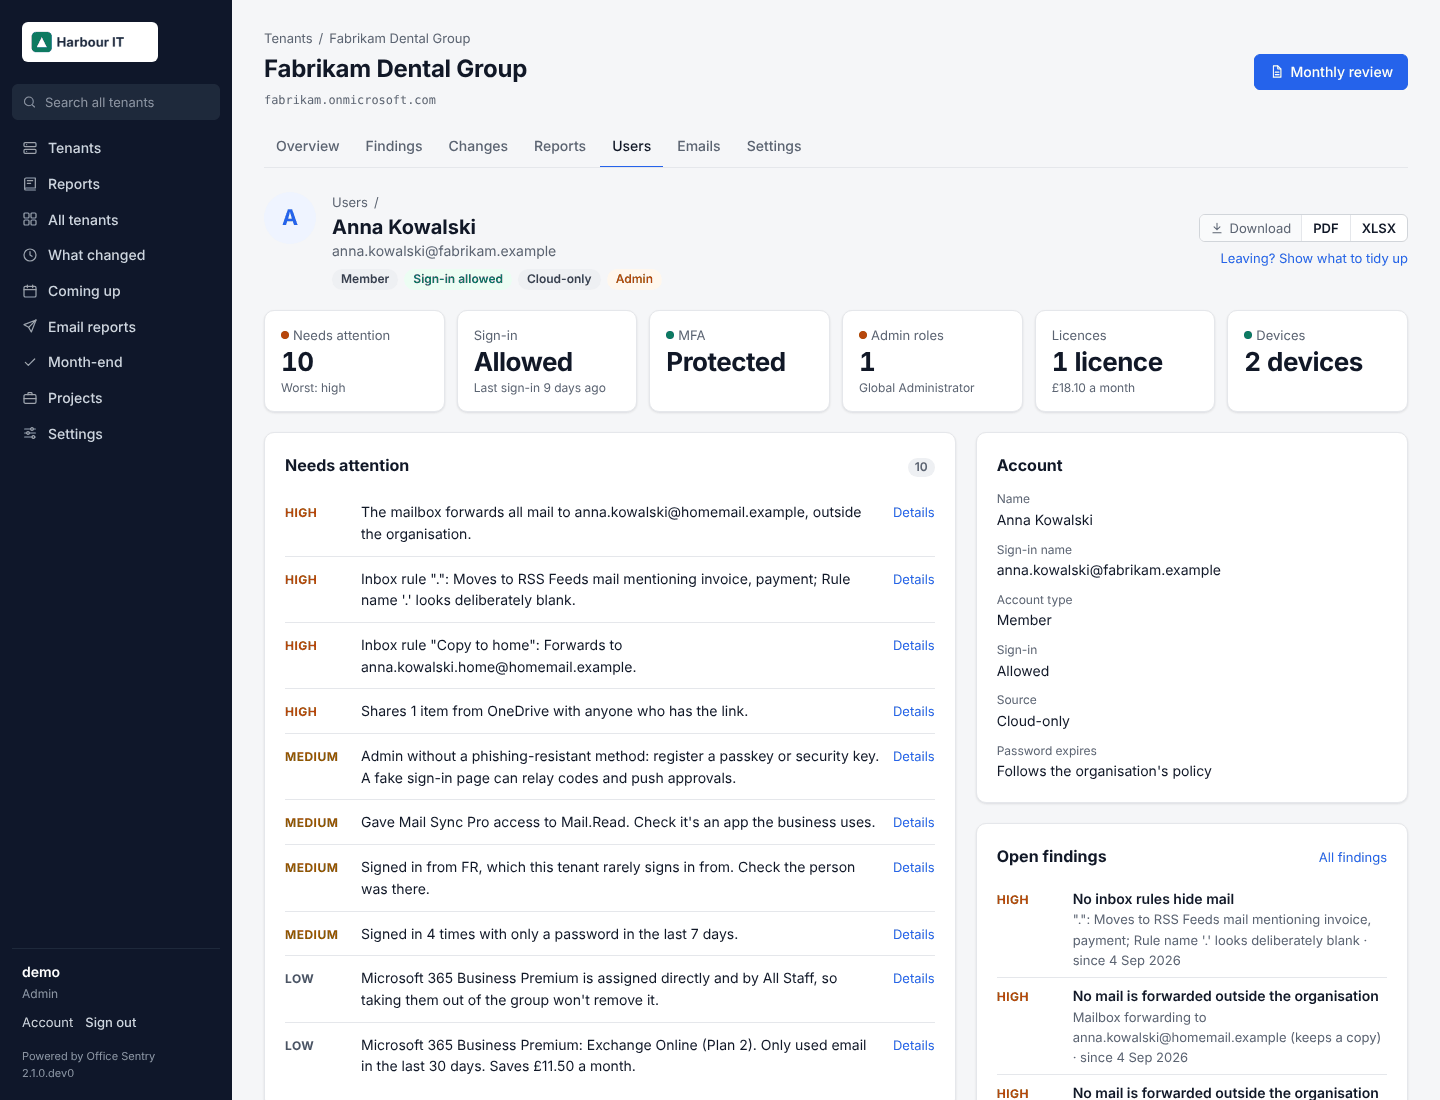
Sign-in, MFA, admin roles, licences, forwarding, devices and sharing for one account, with how it changed.
And every mailbox, group and site
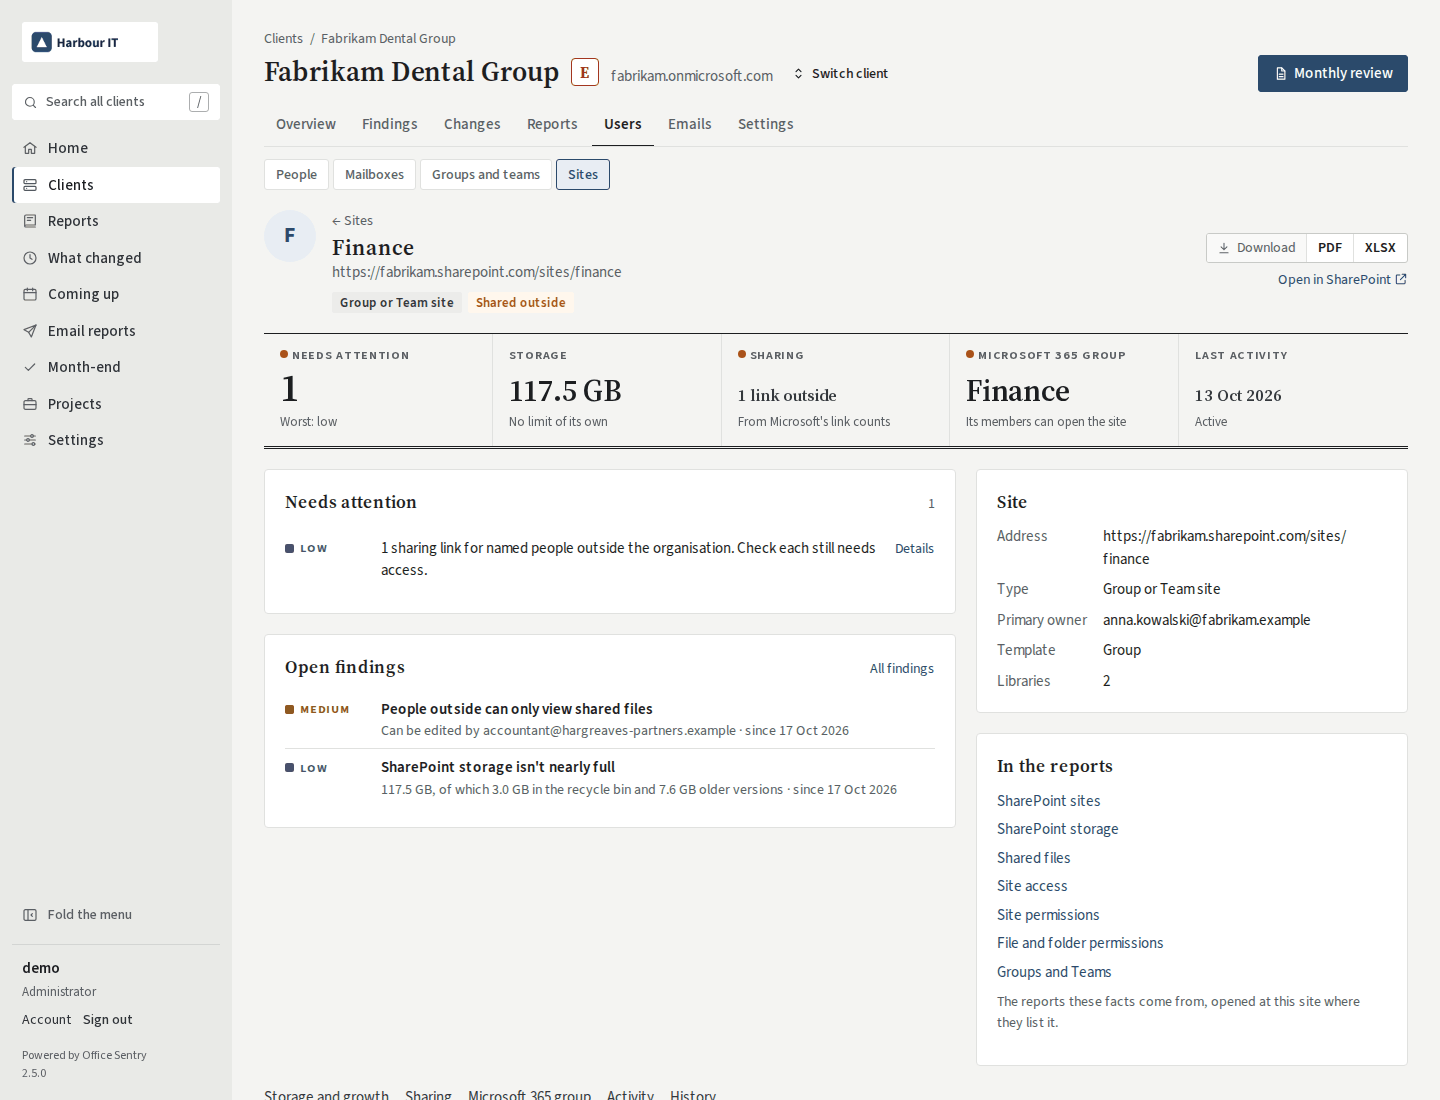
A shared mailbox's size, rules and who can open it; a team's owners, members and what membership gives; a site's storage, sharing and findings.
Projects to recommend
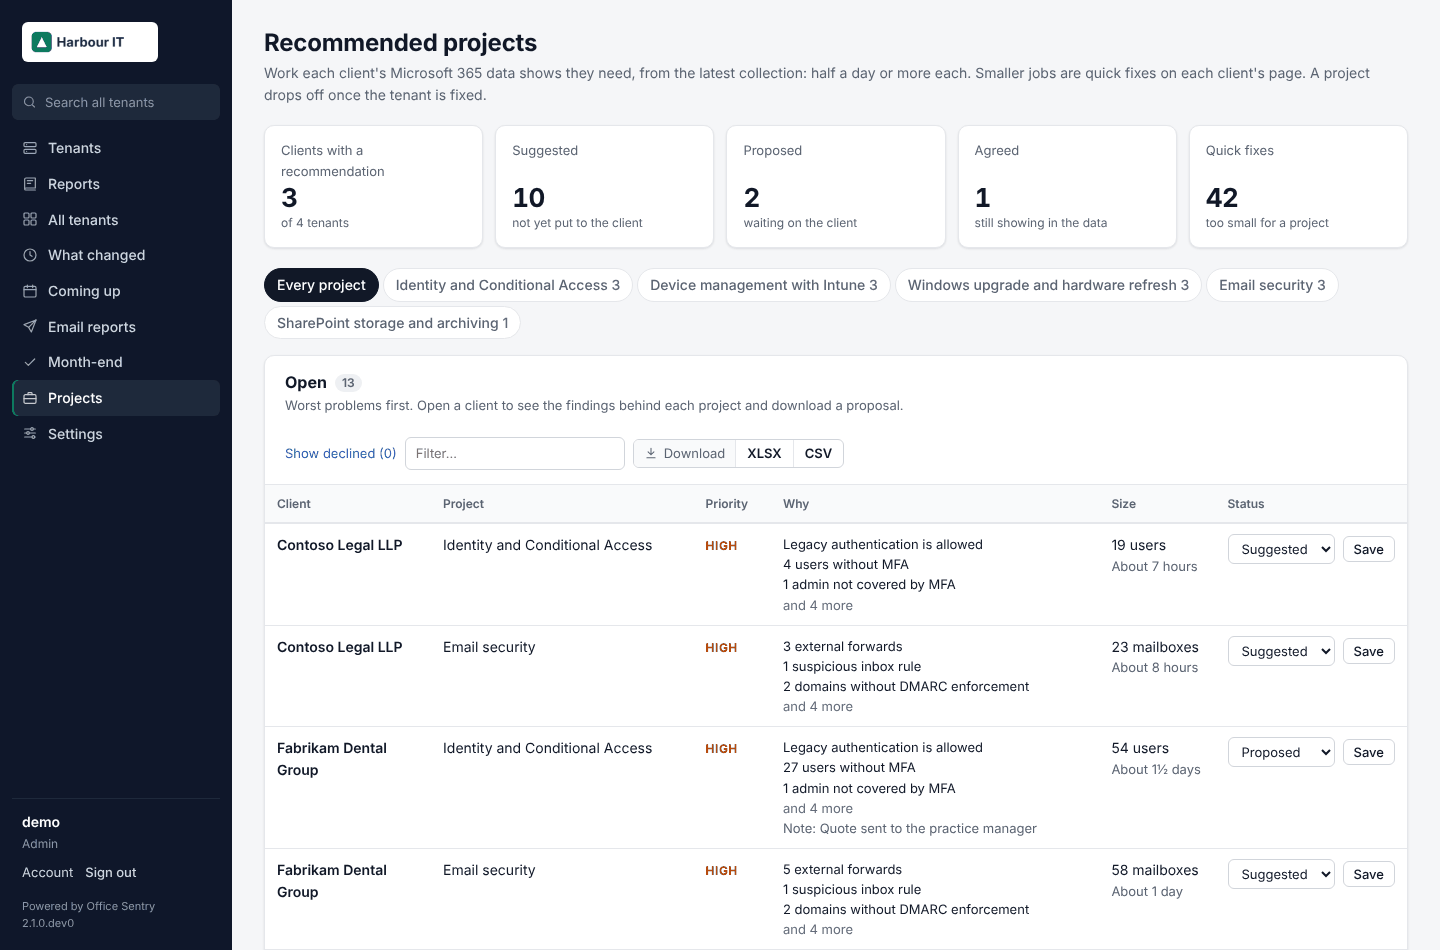
Findings become projects you'd put on a quote, each listing only the work that client needs, with a branded proposal PDF. Repairs are quick fixes, and a project drops off once its findings are fixed.
Emailed reports and alerts
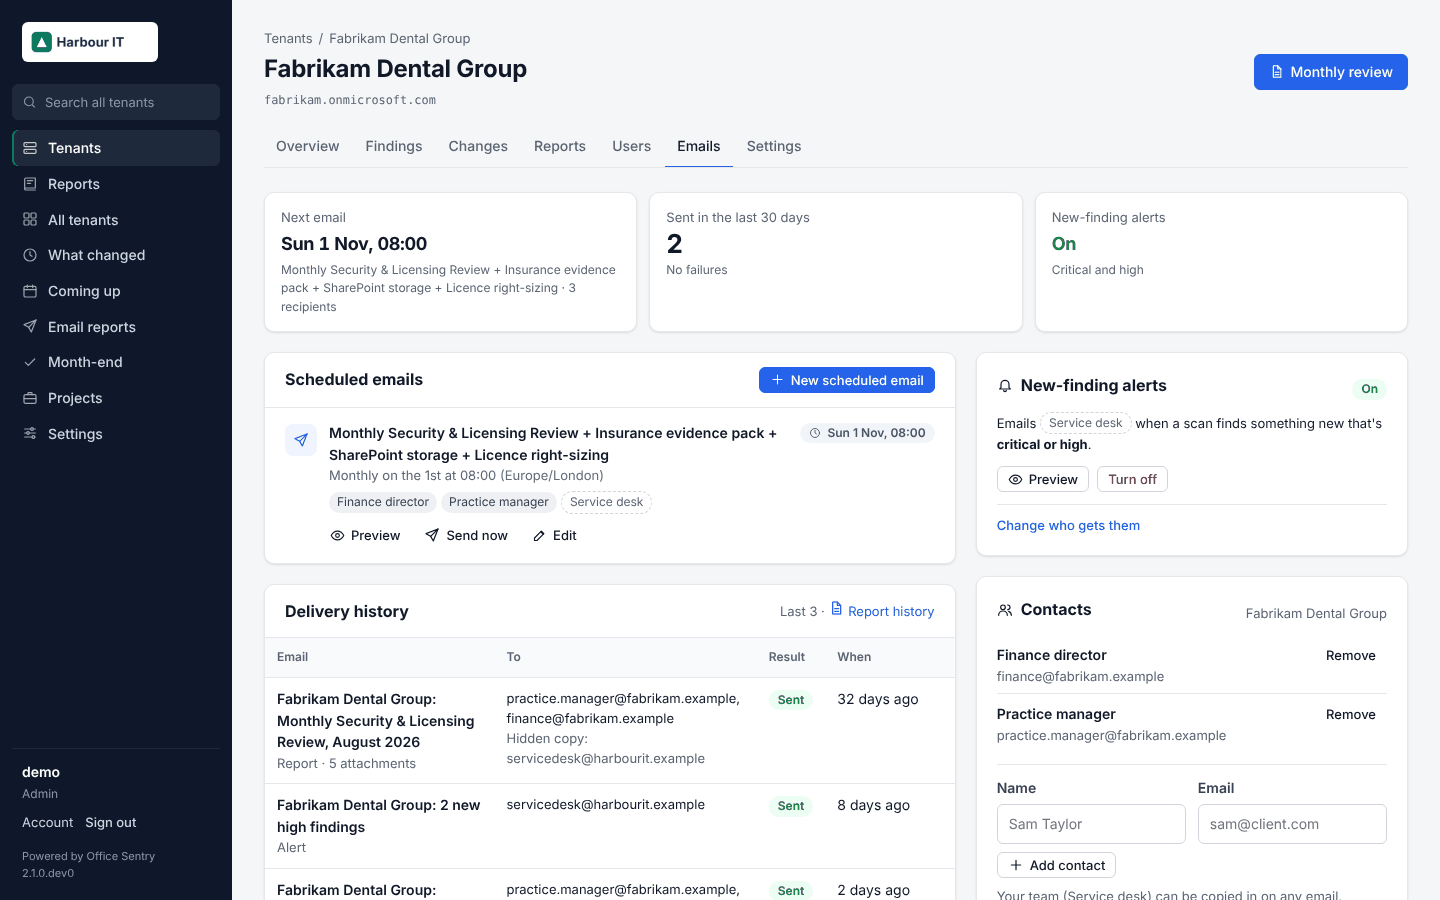
Any mix of reports weekly, monthly or quarterly in the client's timezone, plus alert emails and Teams, Slack or webhook alerts.
A view for your clients
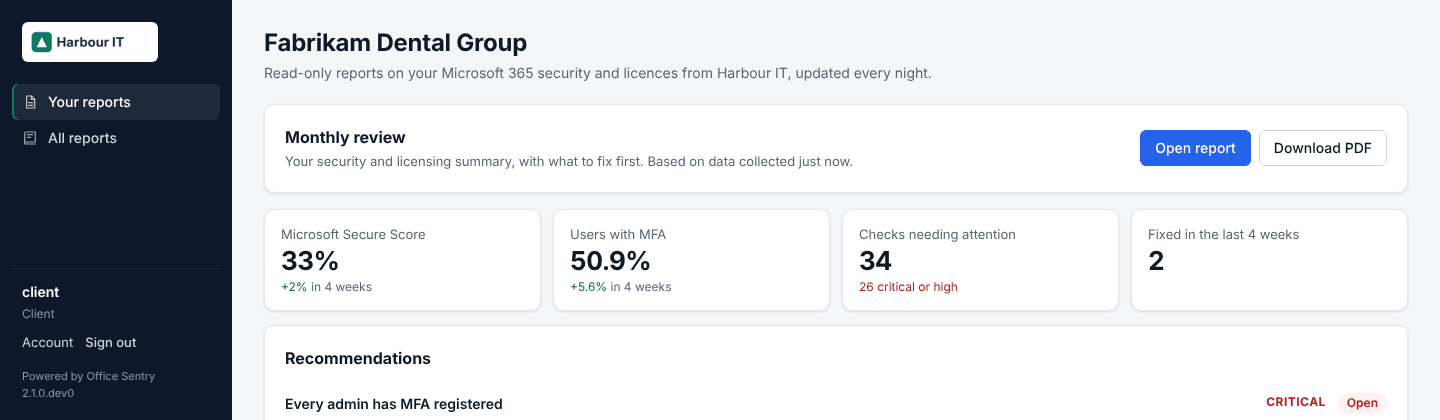
Your clients' people sign in with their own Microsoft work account and see only their own organisation's reports and downloads, never another client or how collection works.
What's coming up
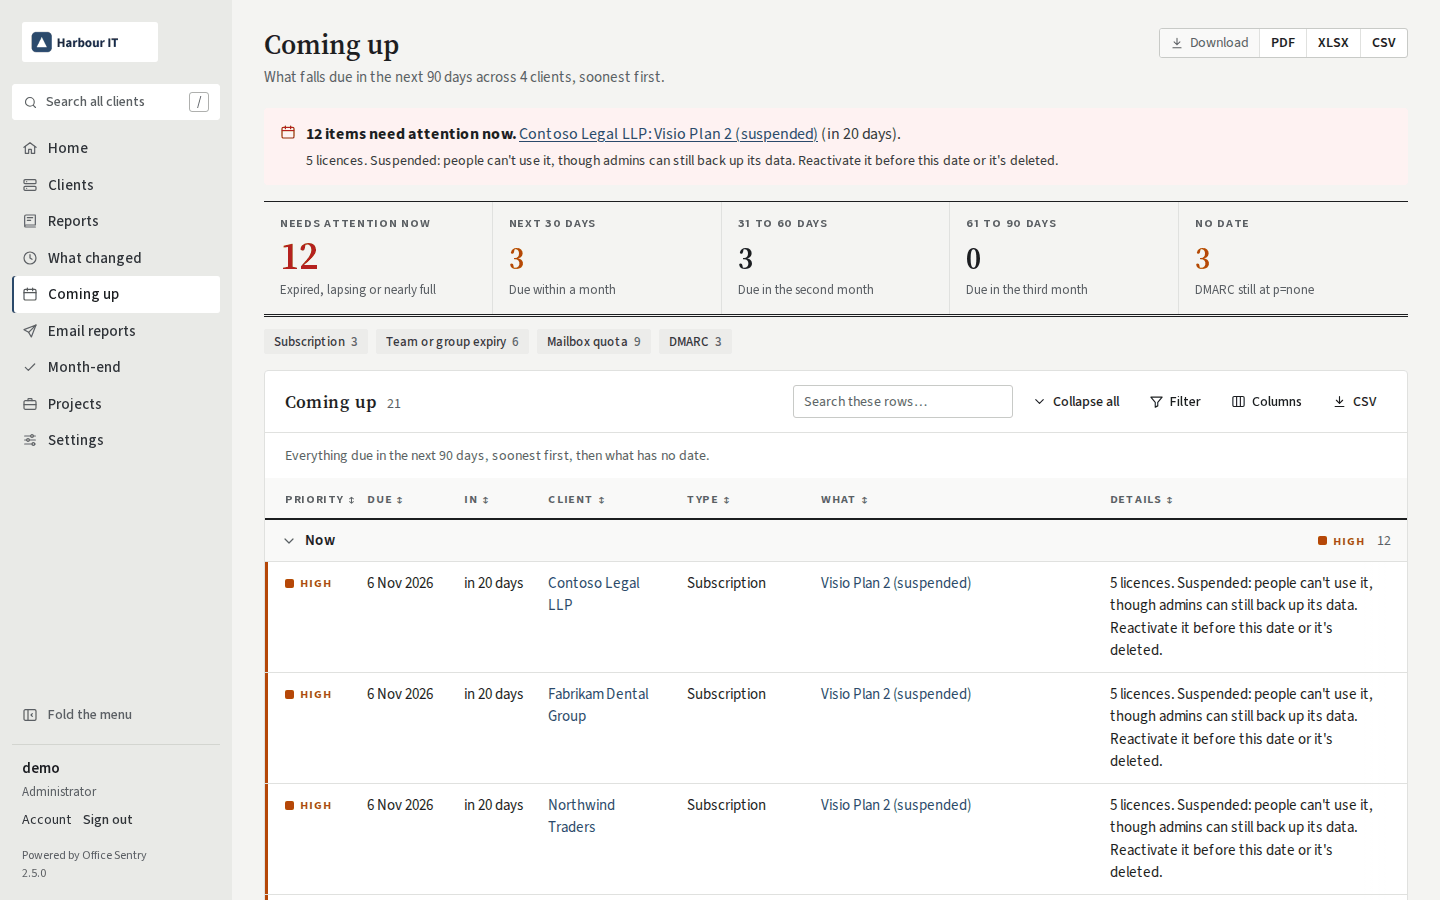
Subscription renewals and trials, expiring app secrets and certificates, mailboxes filling up and risk reviews due in the next 90 days, across every client, with a weekly email.
Activity history beyond 30 days
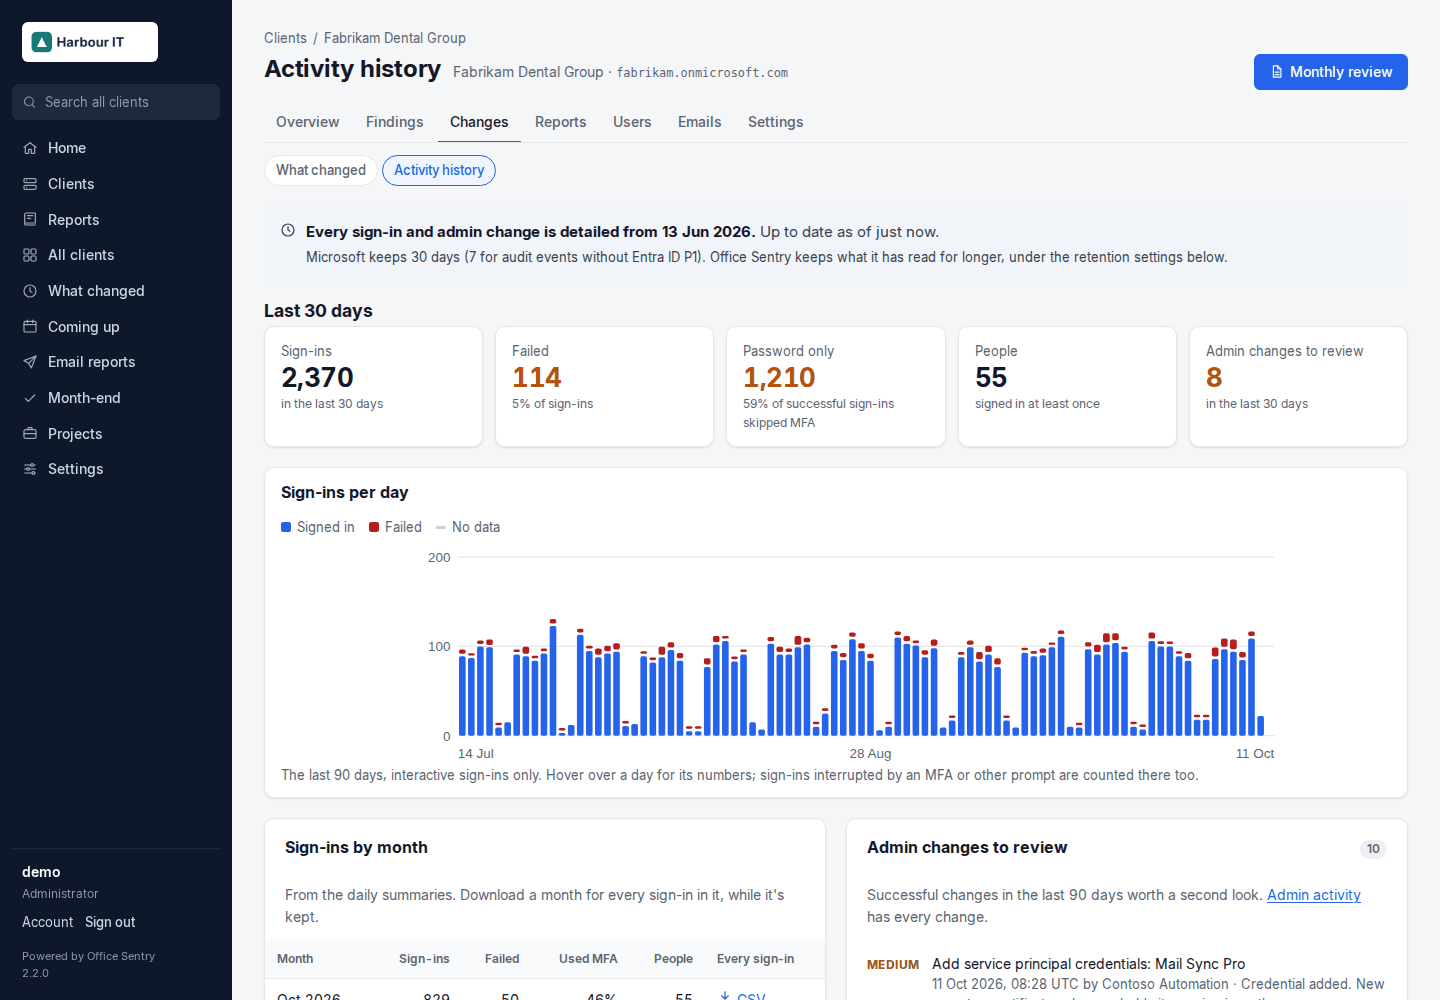
Microsoft keeps sign-ins and admin changes for 30 days. Office Sentry keeps them, by default sign-ins for six months and admin changes for seven years, for each client and each person.
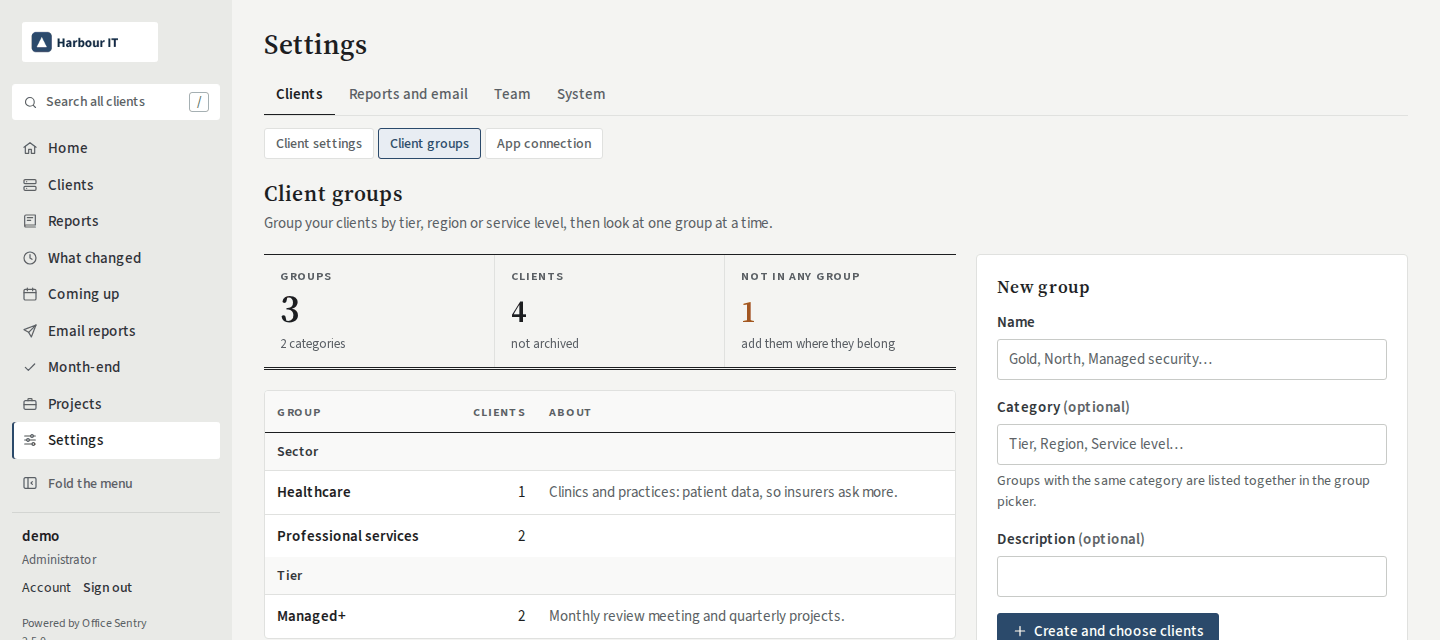
Groups of clients
Group clients by tier, sector or region. Filter the dashboard, every cross-client page and the digest emails by group, and give someone a group instead of a list.
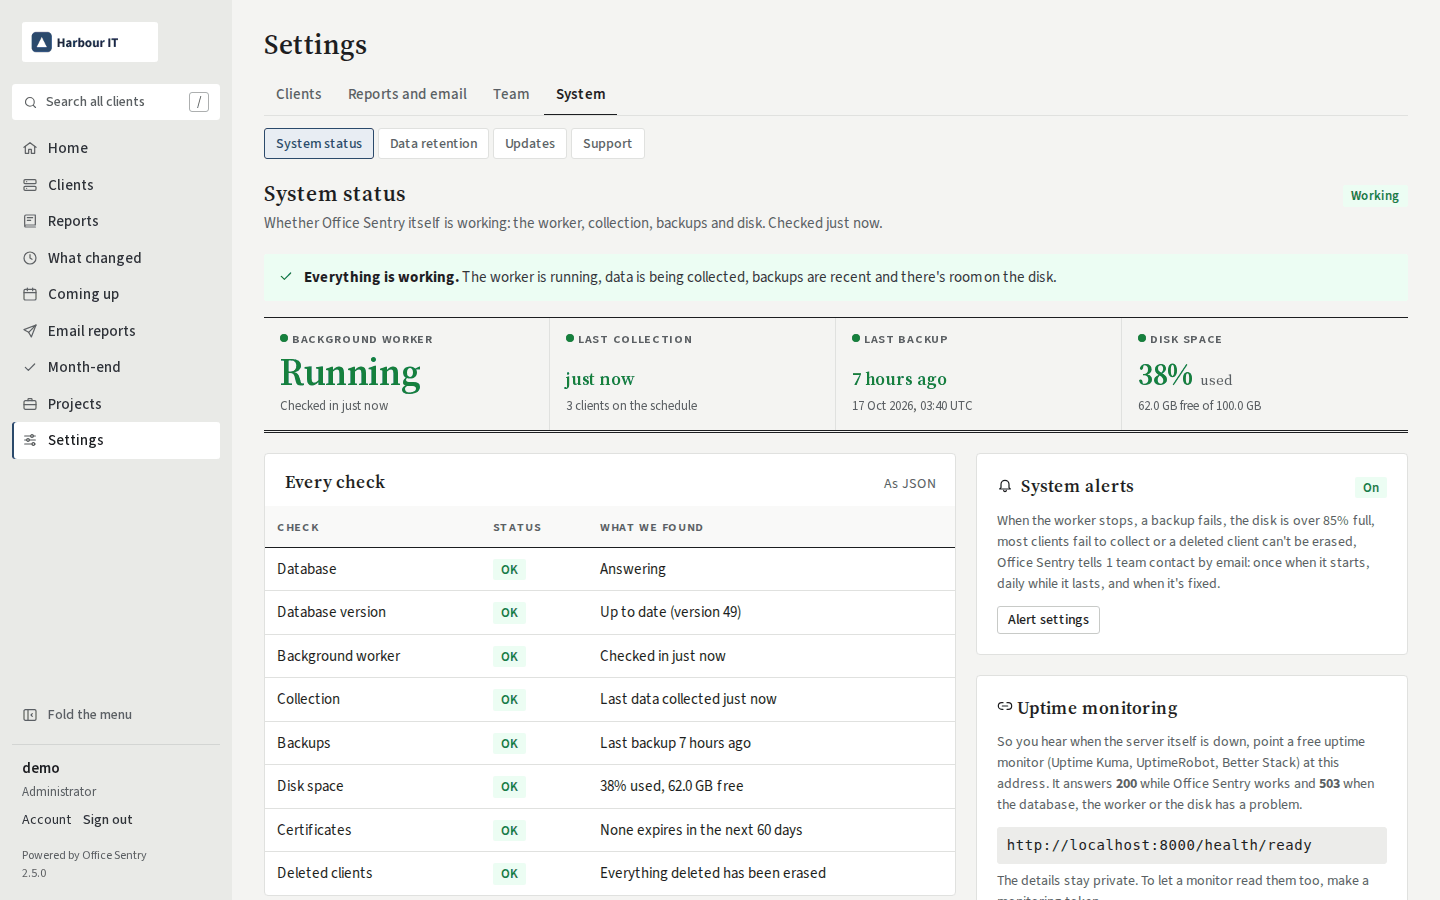
It watches itself
The worker, collections, backups, disk space and certificates are checked all the time, with an email or webhook when something goes wrong and an address for your uptime monitor.
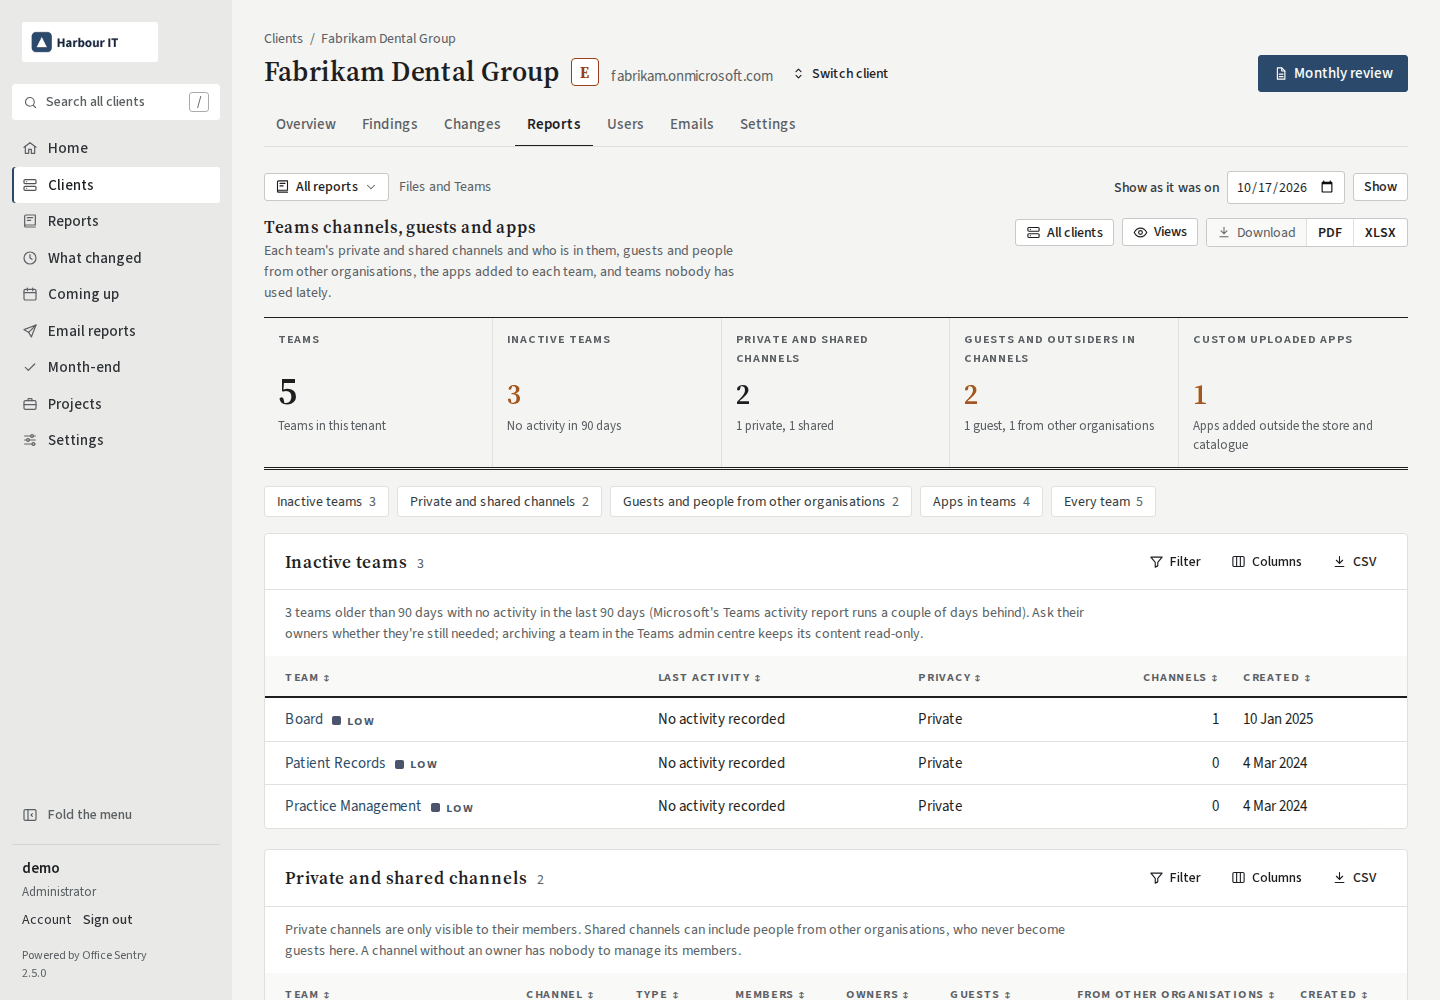
Teams channels, guests and apps
Each team's private and shared channels with their members, the guests and people from other organisations in them, the apps added to each team and teams nobody uses.
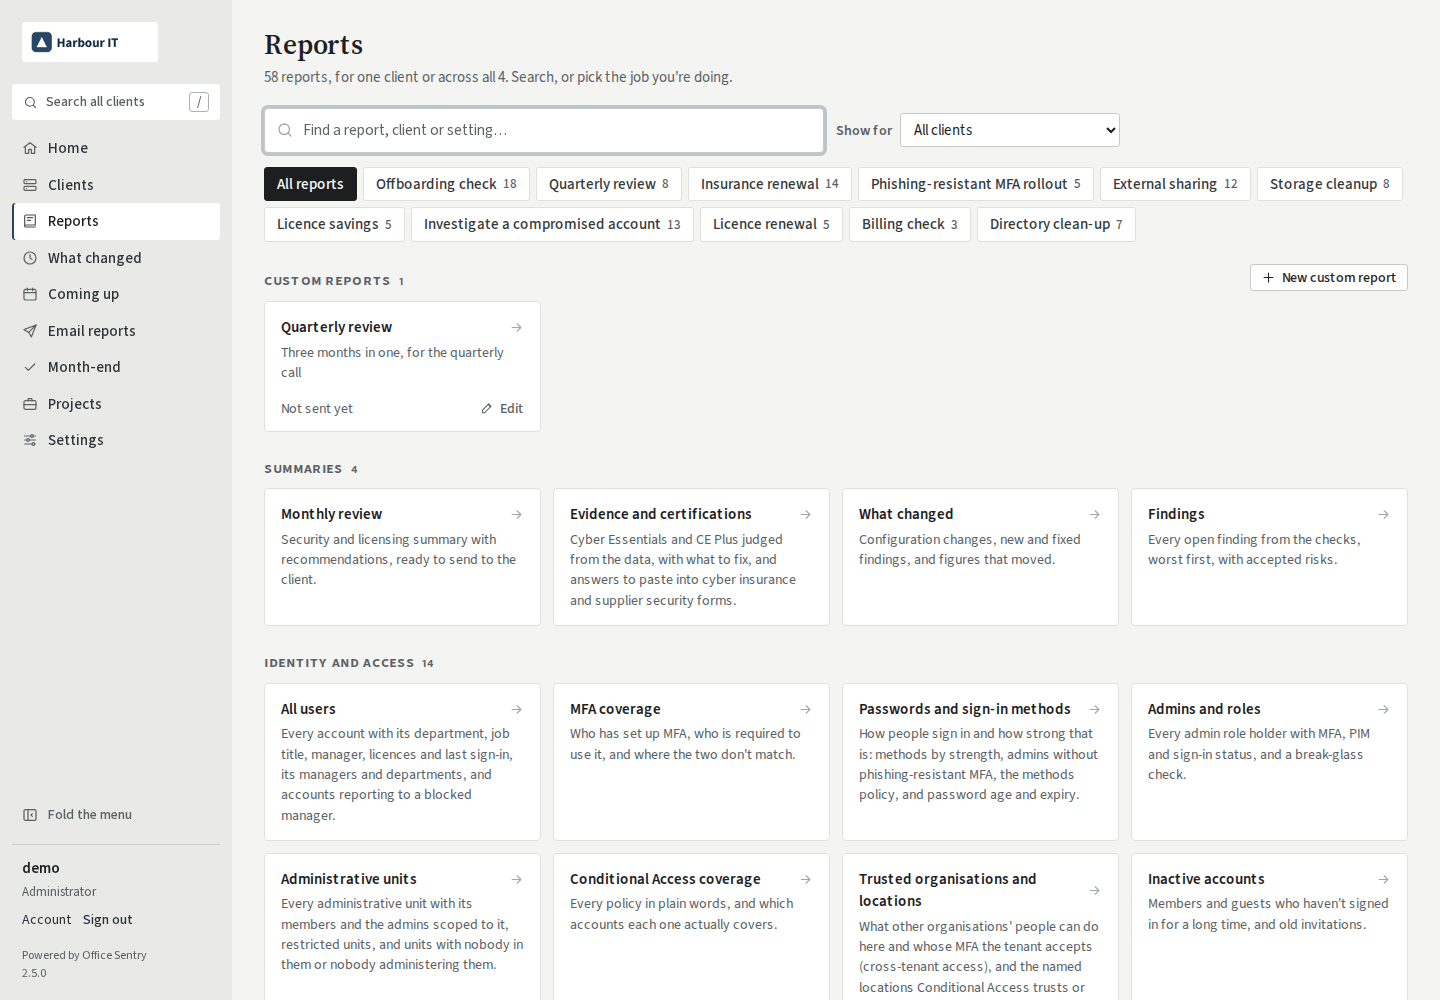
Find a report by the job
The Reports page finds any report by name or by the job you're doing, such as an offboarding check, an insurance renewal or a storage clean-up, for one client or all of them.
Clients that stay connected
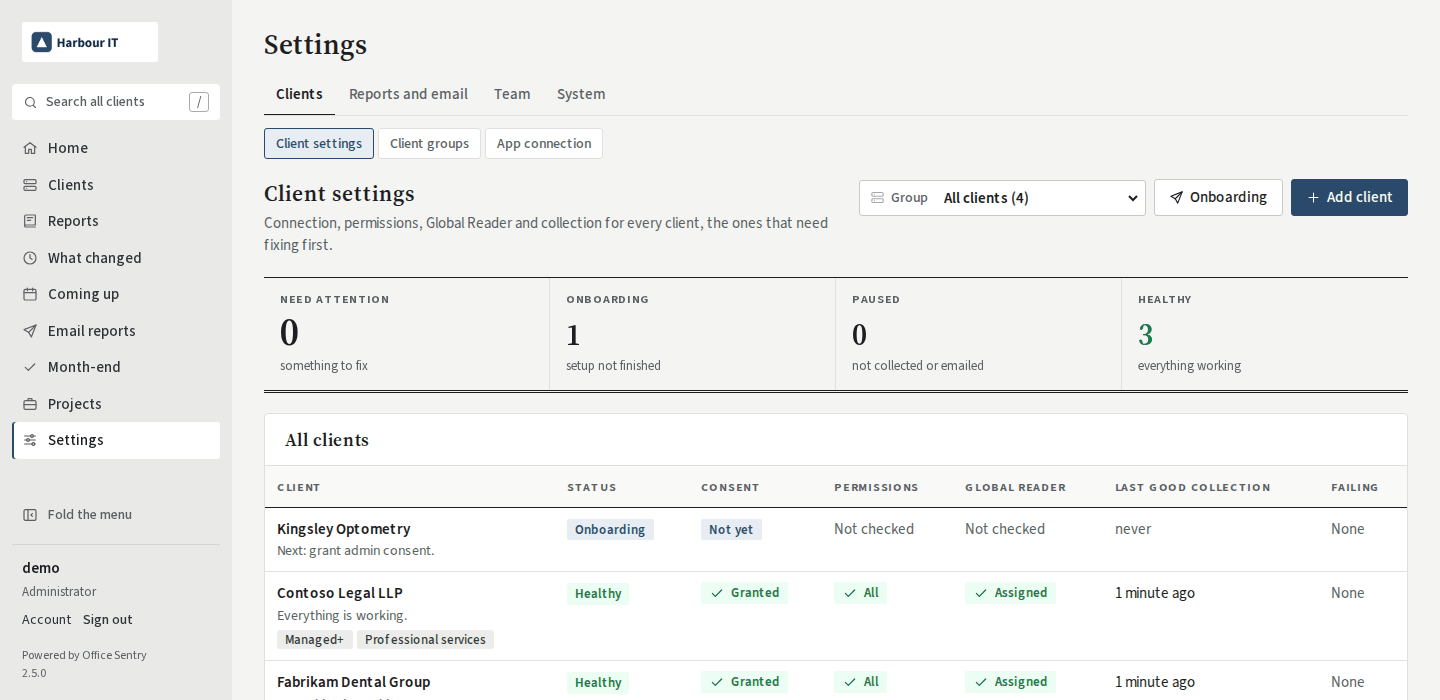
Connection health for every client, worst first. When a release adds permissions, update your app with one sign-in and send each client its What's new page with the approval link.
Licences, renewals and changes
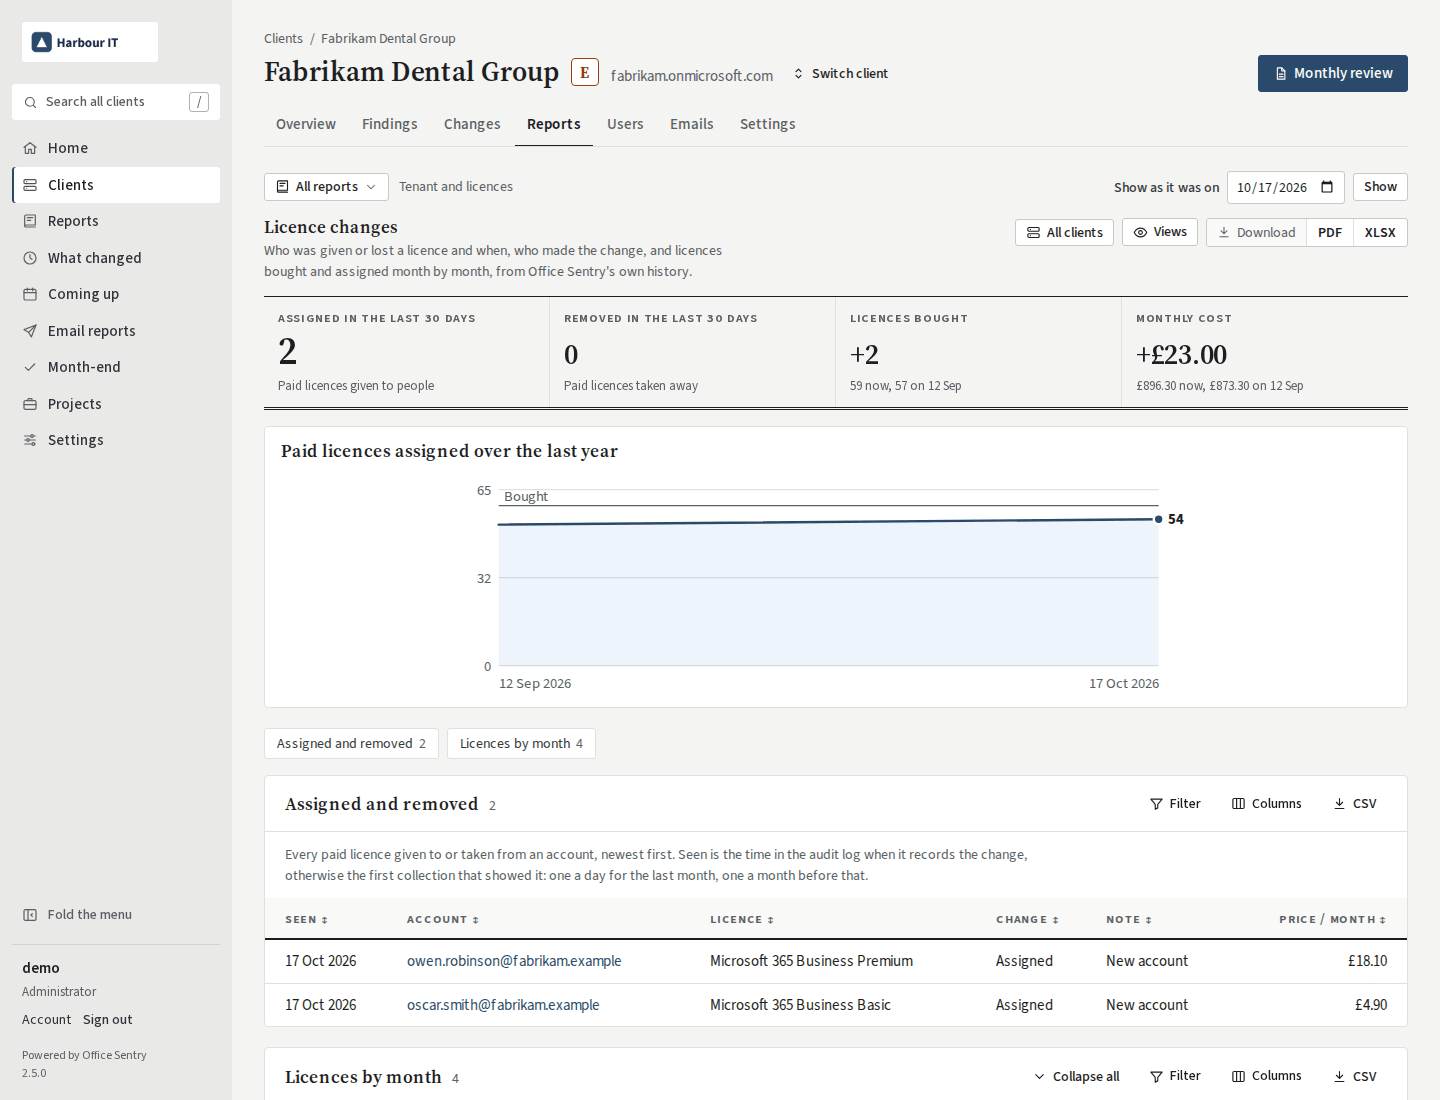
What each subscription costs and when it renews, who was given or lost a licence and who made the change, and licences bought and assigned month by month.
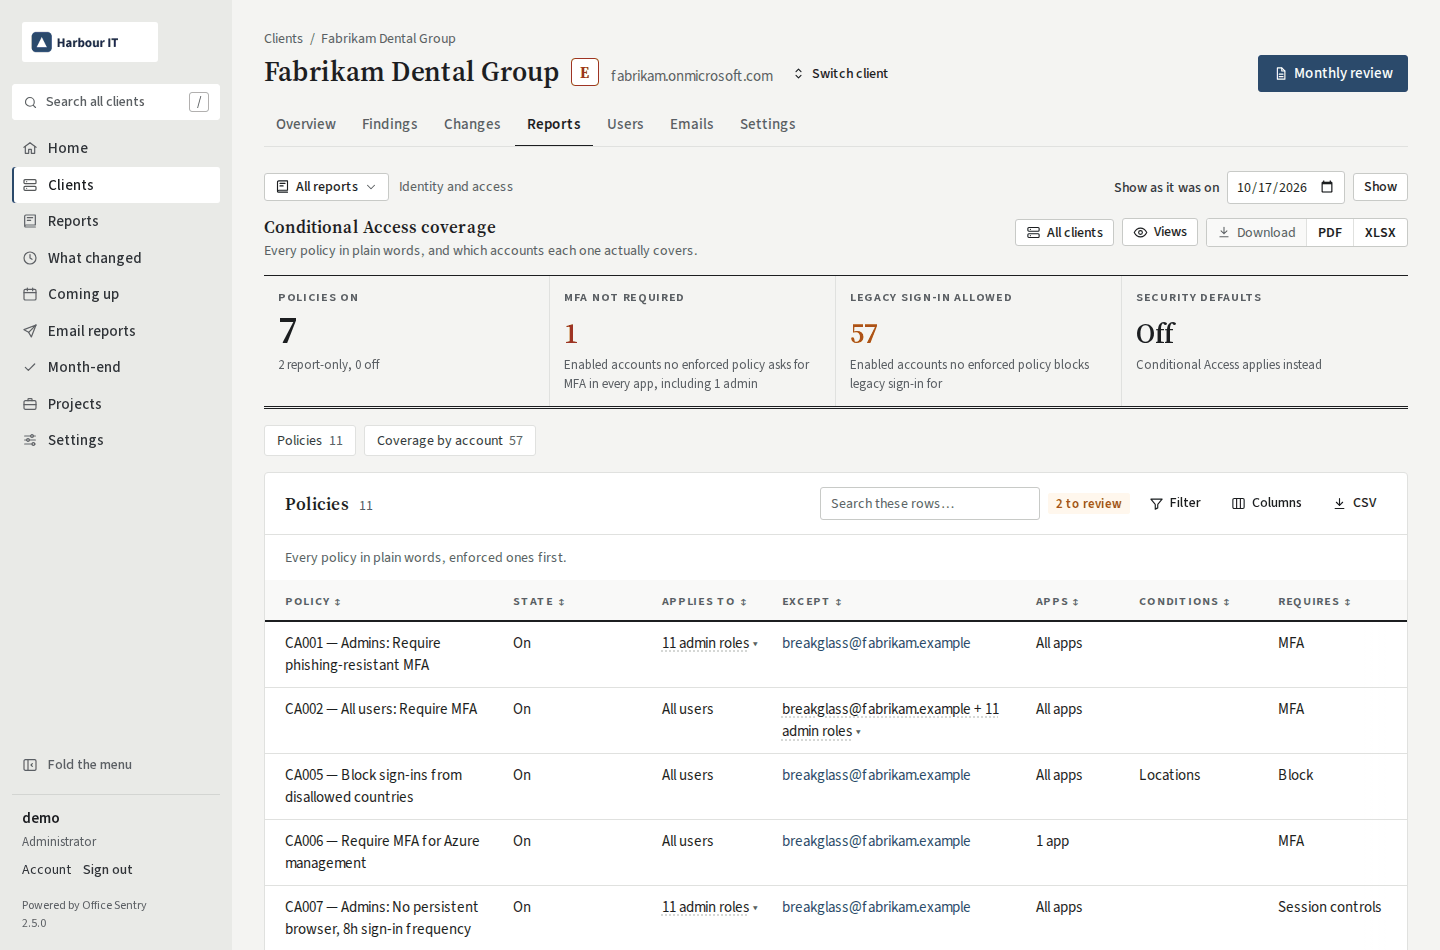
Conditional Access in plain words
Every policy in plain words, and for each account which policy requires MFA, whether legacy sign-in is blocked and which policies exclude it, with groups expanded.
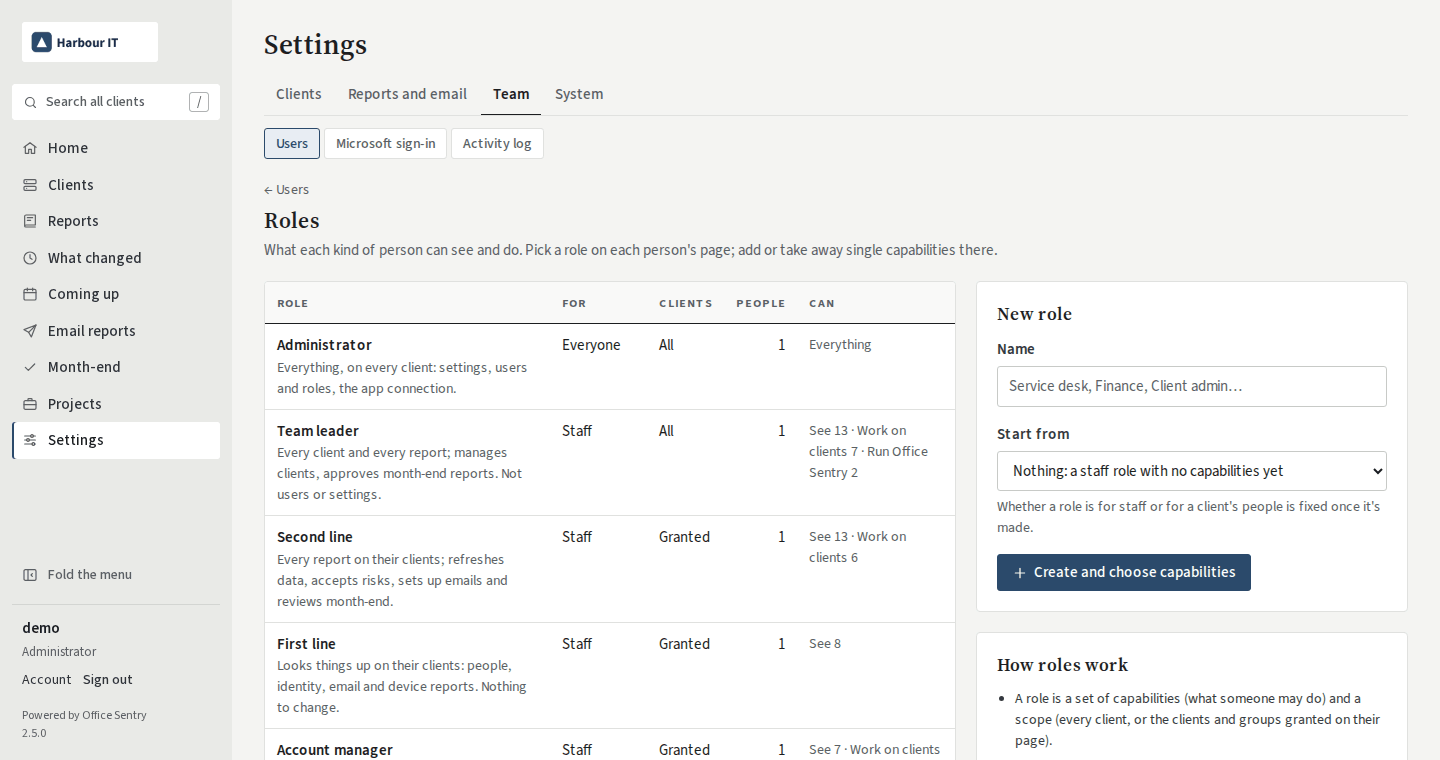
Roles for your team
Seven built-in roles, from Administrator to First line and Auditor, your own roles, and single capabilities given or taken away per person and per client.
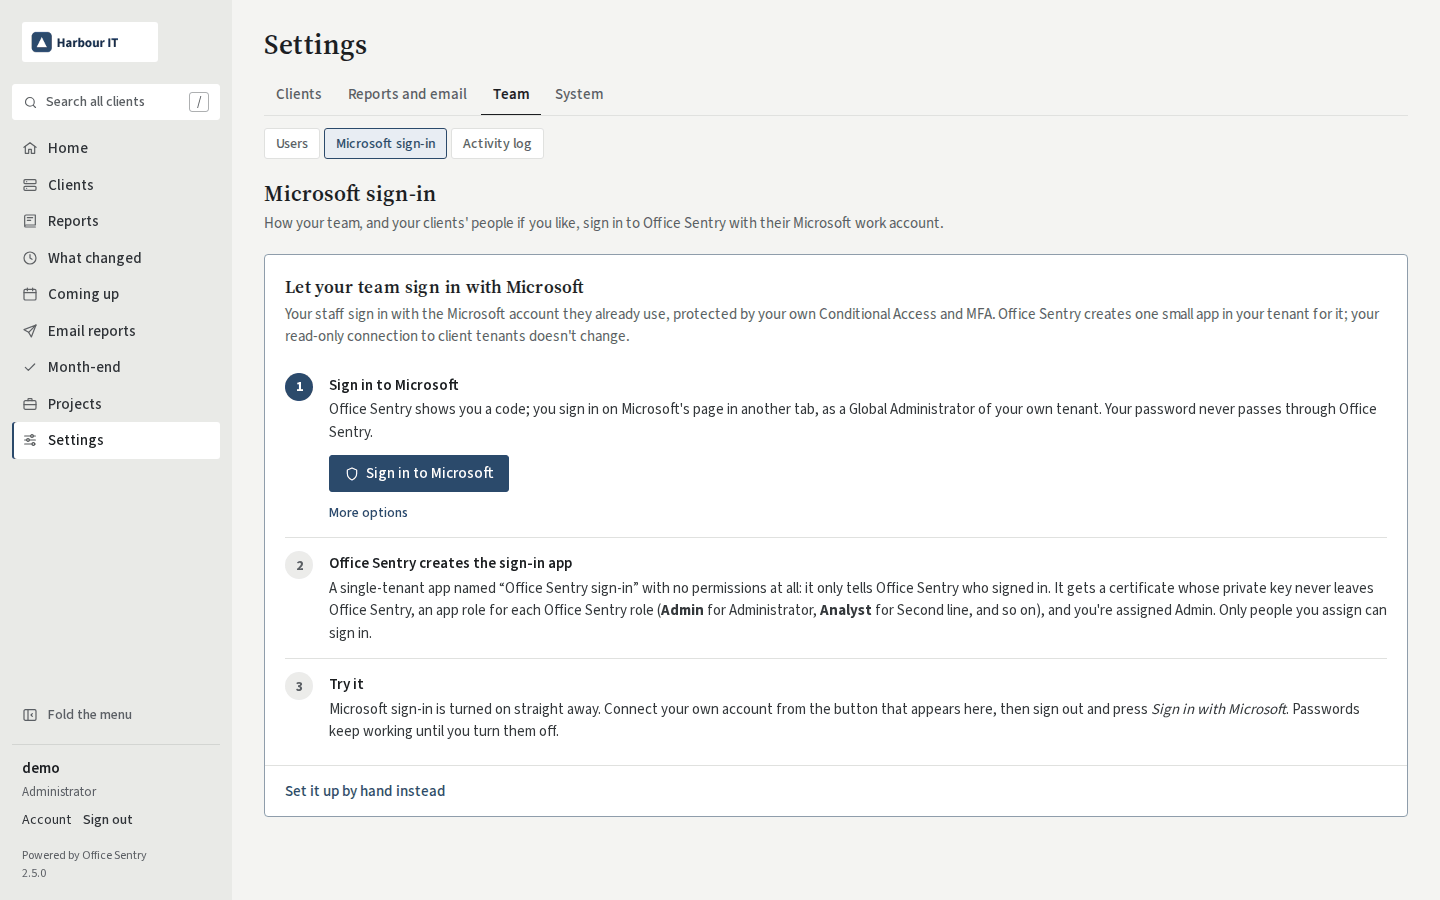
Staff sign in with Microsoft
Your team uses their work account under your own Conditional Access and MFA, with their role assigned in Entra. Passwords stay as the way in if Microsoft sign-in breaks.
Also included
Mail flow by domain Mail received and sent per domain, quarantined and failed mail, and who gets the most spam and phishing.
Intune policies Which platforms have devices but no compliance policy, what each policy requires, paused update rings, and app protection for phones, with who each applies to.
BitLocker recovery keys Which Windows computers have their recovery key saved in Entra ID, read without ever reading the key.
Mail rules and protection Every mail flow rule and connector in plain words, and the spam, phishing and malware policies with whom each covers, with rules that skip the spam filter or copy mail outside flagged.
A support package One zip of versions, settings, health checks and logs to attach to a bug report, with keys, tokens, addresses and client names taken out.
New in 2.5 · 17 October 2026
Act on a finding, grade every client, and get anywhere in a few keystrokes
Every finding opens a sheet with its evidence, history and fix, every client gets a grade from A to E with the rules published, and Today becomes one ledger of what changed overnight.
A finding opens beside the table with the evidence behind it, its history, where else the same check fails, the fix as numbered steps and its project. Copy ready-made ticket text, email the client's contact from your own mail app, keep a note or hand it to a colleague; notes never reach the client.
One letter from A to E, worked out the same way for everyone: the worst of five parts, each its worst open finding after accepted risks. Its page shows what moves each part, twelve month-ends of history and how the client compares with others of its size, none of them named.
One list across every client, worst first, of what changed since yesterday, with what the team fixed. Hand a line to a colleague or snooze it, and a line marks where you last looked.
Timeline, under a client's Changes tab, lays out the year month by month for a review meeting: findings found and fixed, admin changes, reports sent, failed nights and the client's own milestones, beside Secure Score, MFA and open findings at each month's end.
Press / and type "north mfa" for MFA coverage at Northwind, add pdf for the file, or type a page, a setting, a custom report or a person. Search all clients finds clients by name or domain too, and only offers what you can open.
One Clients page, and reports that behave the same way
Clients and All clients are one page, worst first, with any report for every client a menu away. Custom reports live under Reports and send from where you are, a client's Reports tab opens on its catalogue, and every download is named, sorted and laid out the same way.
Also in 2.5: the menu lights the entry every page belongs to, and every browser tab ends with your name; every settings page opens with a Settings heading and says where a sub-page came from; the Flag or Severity column comes first in every CSV and workbook; cross-client PDFs carry your cover and footer, and tables start where they are; clearer wording and dates across the Email, Identity, Files and Devices reports; Devices lists each device's problems as short items you can filter on; SharePoint sites name each site instead of its whole address; a public demo that looks like a real tenant, with the audit log add-on switched on; a diagram of how data flows and how security is checked, in SECURITY.md.
See it for yourself
Open the demo and click around three fictional clients with five weeks of history. Nothing can be changed, and it starts fresh every night.
Read-only in your clients' tenants. The app that reads them asks only for read permissions. The code has no way to write to Microsoft Graph, and only runs Exchange commands that start with Get-.
Sending email is separate and optional. Reports and alerts go out through your own mail server, or through a separate app in your own Microsoft 365 tenant that may send mail and nothing else, limited to one mailbox. It has no access to your clients.
Certificate sign-in, no stored passwords. The app signs in with a certificate whose private key is encrypted in the database. Secrets and private keys can never be downloaded.
Every client kept apart. People see only the clients they're given, and only what their role opens there. Clients see only their own reports, and when they sign in with Microsoft, only from their own organisation's tenant.
Your team signs in your way. Staff sign in with a password and a code from an authenticator app, or with their Microsoft work account under your own Conditional Access and MFA, through a sign-in app in your tenant that has no access to anything else.
Runs on your own server. Your clients' data stays with you. There's no telemetry: nothing is sent to us.
Releases you can check. Each release image carries a signed record of how it was built, so you can check it came from this project's code before you run it. The Update button checks it before it installs anything.
Get started
Up and running on your own server
Office Sentry runs as two Docker containers with everything in one volume. No database server, no Redis.
1
Start it
Download the compose file, set your domain and timezone, and run docker compose up. Guides cover Portainer, a NAS, Kubernetes, Azure, AWS and other clouds.
2
Create the read-only app
Press one button and sign in to Microsoft once: Office Sentry creates the app in your own tenant, with its certificate. A Get started checklist on your home page ticks off each step.
3
Add your clients
Each client approves read access once. The first reports are ready after the first collection.
We're looking for a few MSPs to try Office Sentry with their own clients and say which reports they'd actually send each month. Ask for a walkthrough, a pilot or just a chat.
Nothing. Office Sentry is free software under the AGPL-3.0. You run it on your own server; a small cloud server is enough for most MSPs.
Can it change anything in a client's tenant?
No. It only asks your clients' tenants for read permissions, and its code can't write to Microsoft Graph or run Exchange commands other than ones that read. The one thing it sends is your own email: reports and alerts, through your mail server or a separate app in your own tenant that can only send mail.
Does it read anyone's email?
No. It reads settings, mailbox details such as size, forwarding and permissions, and inbox rules, never message contents. What Office Sentry reads lists every permission, written for your clients.
Can my team sign in with their Microsoft accounts?
Yes. Office Sentry creates a small sign-in app in your own tenant, with no access to anything else, and your staff sign in under your Conditional Access and MFA. Their role comes from Entra at every sign-in; which clients they see is still set in Office Sentry. Staff sign-in has the steps.
Can my clients sign in with their own Microsoft accounts?
Yes. Add each client's contacts by their work address and they sign in with the account they already use, under their own organisation's MFA, from their own company's tenant only. Nobody is invited into your tenant as a guest, and they only ever see their own company's reports. Client sign-in has the steps.
How do I update it?
Settings → Updates lists every newer release with its notes and anything to do first. Turn on the optional updater and its Update button installs a release, after checking it's genuine, and goes back to the old version by itself if the new one doesn't start. Updating by hand with Docker works as well. Updating has both.
Where is the data kept?
On your own server, in a database and the activity history beside it, which its backups copy, encrypted off the server if you like. Office Sentry has no telemetry, so nothing is sent to us: the only thing it asks for is GitHub's list of releases, once a day, which an admin can turn off.
How is it different from Microsoft's own admin centres?
Microsoft shows one tenant at a time, in its own words, with little history. Office Sentry collects every client every night, keeps the history, compares it month by month and across clients, and turns it into branded reports.
Can it replace AdminDroid, CIPP or another paid tool?
For reporting, yes: monthly client reviews, evidence for Cyber Essentials, ISO 27001 and insurers, 53 detail reports and 71 checks across every client, with history. It never changes a tenant, so for creating users or applying settings keep a management tool such as CIPP beside it. How it compares sets out what each is good at.